

Supply chain security template
NIS2 supplier questionnaire template
Questions for suppliers and service providers on supply chain security under Section 30 BSIG, each with its reference and the matching evidence.
What the file contains
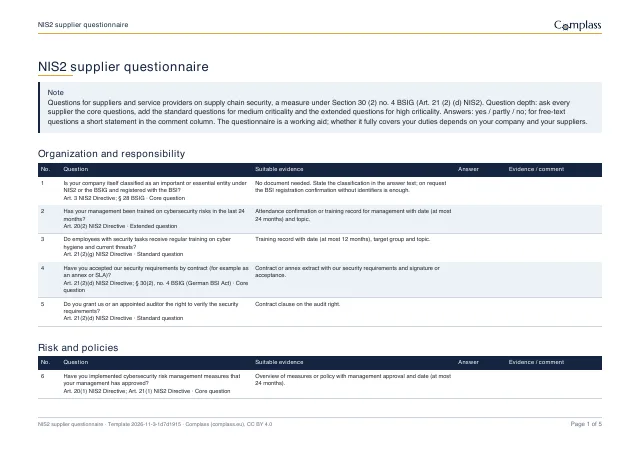
31 questions for suppliers and service providers in 8 areas, each with its reference, question depth and the evidence that fits as proof. The supplier fills in answers, evidence and comments.
- Organization and responsibility 5 rows
- Risk and policies 2 rows
- Incidents and reports 4 rows
- Access and identities 4 rows
- Operations, patches and vulnerabilities 7 rows
- Product and development security 1 rows
- Continuity and backup 4 rows
- Own supply chain 4 rows
Template version 2026-11-3-1d7d1915 · content as of 1 November 2026 · Excel (XLSX) 102 KB · Word (DOCX) 7 KB · PDF 38 KB
This template exists in German and English; you get the English version.
This template is not legal advice. It does not replace checking which requirements apply to your company and does not guarantee any audit or certification result. License CC BY 4.0
How to use the file
Classificar fornecedores
Core questions go to every supplier, standard questions in addition for medium criticality, extended questions for high criticality.
Send the questionnaire
As Word or Excel, with a deadline for the reply. The "Suitable evidence" column tells the supplier which proof is enough.
Review the answers
Gaps become measures with a deadline or supply chain risks. Decide when you will ask the supplier again.
The portal takes it from there
In Complass the supplier answers the same questionnaire in their own free account and uploads evidence. You review each answer, completion seals the assessment with a checksum, and gaps become measures or risks. If you wish, Complass invites the supplier again automatically before the next review.
Perguntas frequentes
Does the questionnaire fully cover Section 30 BSIG?
It supports the supply chain security measure under Section 30 (2) no. 4 BSIG. Whether it fully covers your duties depends on your company and your suppliers; it is a working aid, not legal advice.
Do we have to ask every supplier?
The law names no minimum number; it asks for suitable, proportionate and effective measures (Section 30 (1) BSIG). Record all suppliers and ask in depth according to risk.
Is the supplier's ISO 27001 certificate enough?
It is strong evidence if its scope covers the service you receive. So check the scope and the Statement of Applicability, not just the certificate.
Does this also apply to indirect suppliers?
Section 30 (2) no. 4 BSIG names direct suppliers and service providers. The questionnaire therefore asks about their subcontractors instead of assessing everyone further down yourself.
Teste o Complass com os seus próprios dados
Crie o seu próprio acesso de teste, se quiser com um projeto de exemplo por referencial. Se preferir ver primeiro o Complass, peça uma demonstração.