

This guide shows the inputs, the procedure in five steps and a template for the minutes. The standard is paraphrased in our own words, and the examples are invented.
What clause 9.3 requires
- Planned intervals. The standard sets no cycle. At least one meeting a year is common.
- Top management. It carries out the review itself. The CISO may prepare it.
- Defined inputs. Clause 9.3.2 lists the topics that feed into the review.
- Decisions. The results include decisions on improvements and on changes needed to the ISMS.
- Evidence. The results must be available as documented information.
Before a certification audit, certification bodies usually expect a completed management review. The standard itself sets no time for it.
The inputs at a glance
Structure the report and minutes by these inputs, and the auditor finds everything at once.
| Input | Question for management | Typical source |
|---|---|---|
| Earlier reviews | What became of the last decisions? | Action list |
| Internal and external issues | What has changed around us? | Context document |
| Interested parties | What do customers, authorities and others expect today? | Customer requests, new laws |
| Nonconformities and corrective actions | Which findings are open? | Findings register |
| Measurement results | How are the key figures developing? | Key figures under 9.1 |
| Audit results | What did internal and external audits show? | Audit reports |
| Objectives | How far are the security objectives met? | Objectives plan under 6.2 |
| Feedback | What do stakeholders report back? | Customers, staff, service providers |
| Risks | What is the risk situation, how far is the treatment plan? | Risk register |
| Improvement | Where can the ISMS get better? | Suggestions, lessons from incidents |
The procedure in five steps
- Set the date. Plan it after the internal audit so that the results feed in.
- Prepare the report. The CISO summarizes the inputs on a few pages and names the open decisions.
- Review. Management goes through the inputs and judges: is the ISMS suitable, adequate and effective?
- Decide. Record every decision with an owner and a date.
- Follow up. The decisions go into the action plan and are the first input to the next review.
Template for the minutes
Copy the table into your own template. The entries on the right are invented examples.
| Section | Example |
|---|---|
| Date and participants | 12 March, managing directors, CISO, head of IT, head of production |
| Status of earlier decisions | 5 of 6 done, segmentation of hall 2 postponed |
| Changes around us | Major new customer asks for evidence, new plant planned |
| ISMS performance | Open findings 7, training rate 92% |
| Audits | Internal audit: 2 nonconformities, 5 recommendations |
| Objectives | 3 of 4 objectives met |
| Feedback | Two customer questionnaires, no complaint |
| Risks and treatment | Remote maintenance still high, treatment plan 70% done |
| Improvements | Extend the incident exercise to the night shift |
| Decisions | Budget for remote maintenance released, owner: head of IT, date: 30 June |
| Overall judgment | ISMS suitable and adequate, improve effectiveness for remote maintenance |
The most common mistakes
- Only taking note: The minutes contain not a single decision.
- Without management: The CISO reviews alone and management only signs.
- No follow-up: Decisions from last year no longer appear anywhere.
- Wrong order: The meeting comes before the internal audit, so its results are missing.
Example from industry
The example is invented. An automotive supplier puts the review on the agenda of the management meeting. Two hours are enough because the CISO circulates the report a week before.
- Insight: Customers ask more often about OT security, but production is only partly in scope.
- Decision: The scope grows in the next cycle, and one position is added.
- Evidence: Minutes with owners and dates, tasks in the action plan.
Checklist
- The date falls after the internal audit.
- Top management takes part.
- All inputs under clause 9.3.2 are covered.
- The overall judgment on suitability, adequacy and effectiveness is in the minutes.
- Decisions on improvements and changes are made.
- Every decision has an owner and a date.
- The minutes exist as documented information.
- The status feeds into the next review.
The management review in Complass
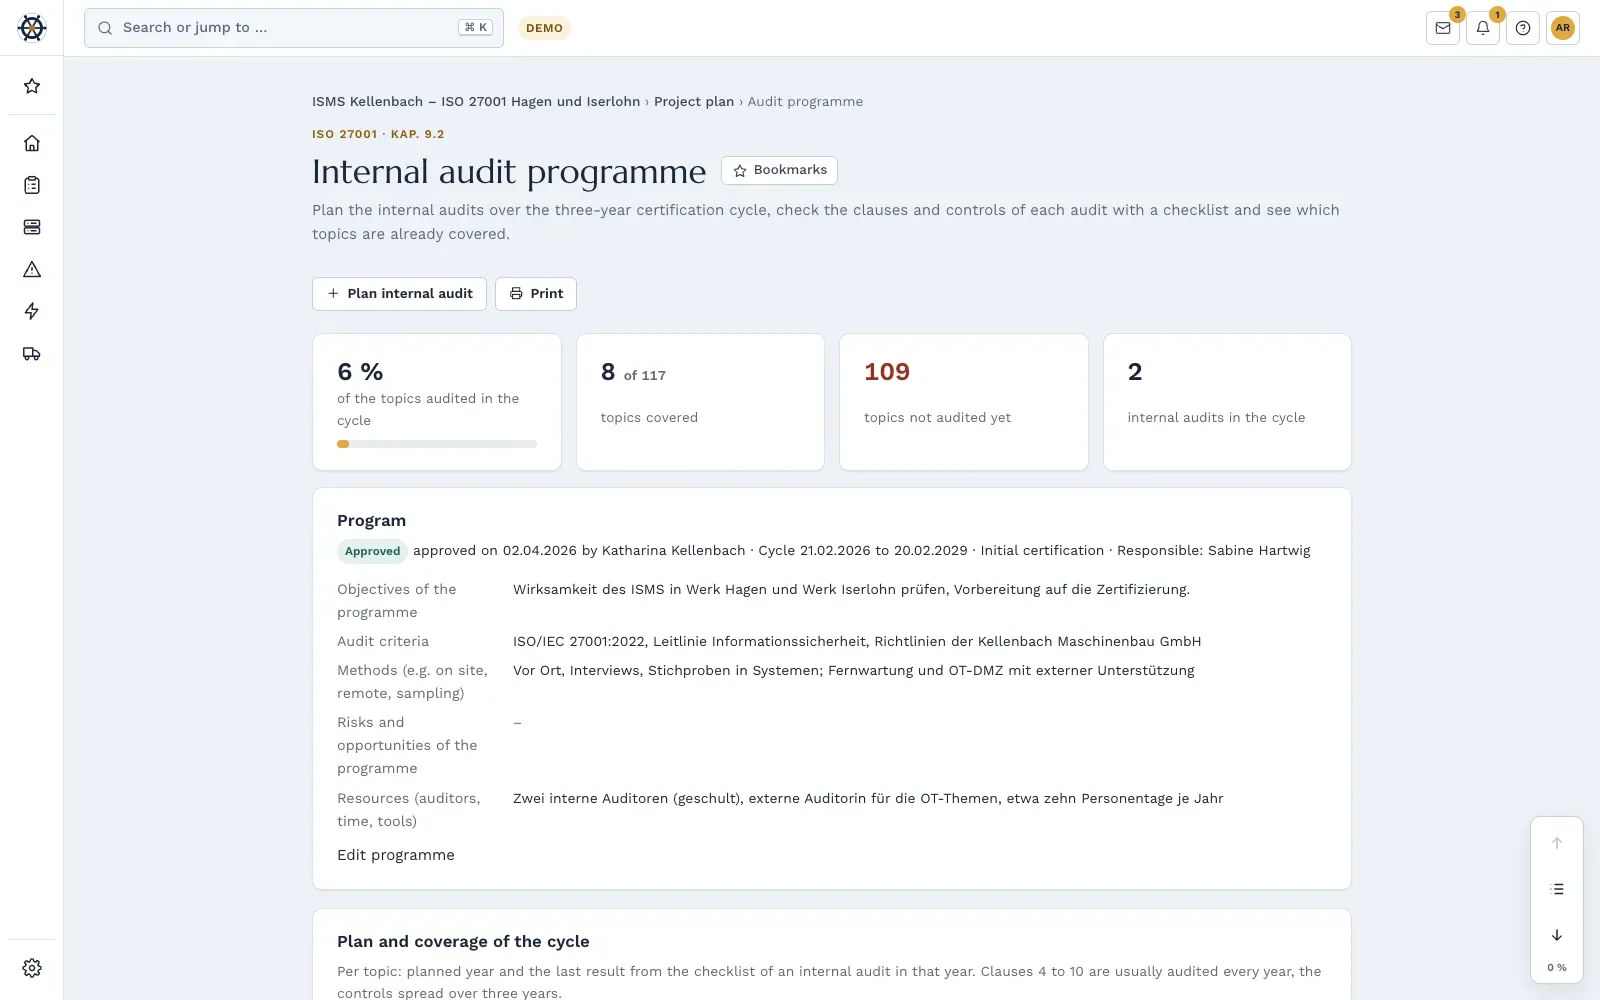
No more collecting figures before the meeting. Complass builds the report from what is already in your ISMS:
- Management report: A PDF structured like clause 9.3, with key figures and trends, also as PowerPoint.
- Inputs: Complass shows which inputs the report covers. You state changes around you with yes or no.
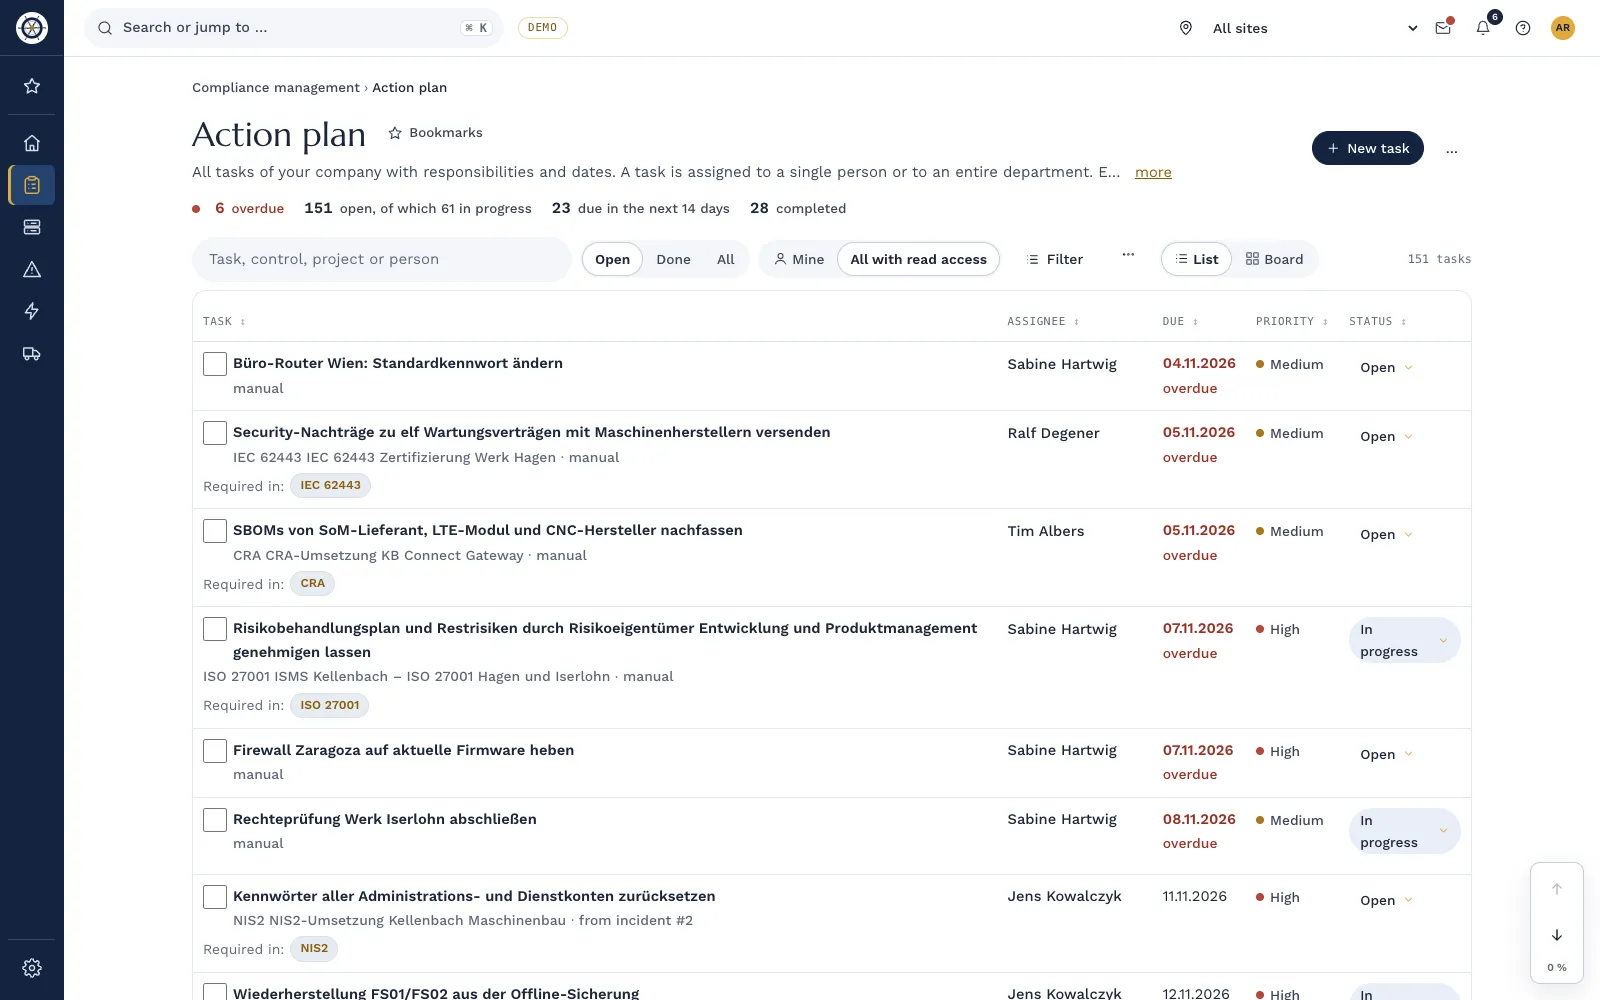
- Results: Every result becomes a task in the action plan, with an owner and a deadline.
- Findings: You record nonconformities directly in the findings register.
- Confirmation: The participating members of management confirm in person. The status is then filed as evidence.
- Template: The ISO 27001 module contains a document for the minutes with guidance.
Frequently asked questions
How often do we have to carry out the management review?
The standard requires planned intervals and sets no cycle. At least once a year is common, and more often after major changes.
May the CISO carry out the review alone?
No. Clause 9.3 addresses top management. The CISO prepares and reports.
Does management have to sign the minutes?
The standard does not require a signature. It has proven useful as evidence of participation and decisions.
Can we combine it with the ISO 9001 review?
Yes. Keep the ISMS part clearly visible so that all inputs of clause 9.3.2 can be seen.
Does the management review replace oversight under § 38 BSIG?
No, but it supports it. § 38(1) BSIG (German BSI Act) requires oversight of the measures under § 30 BSIG. In our view one review a year is hardly enough for that. Our guide on § 38 BSIG shows a quarterly rhythm.
In a demo we show you how ISMS data becomes a report and how decisions become tasks.
Request a demo Try it for 14 days
Read more
- Guide "Preparing an ISO 27001 internal audit"
- Guide "ISO 27001 mandatory documents at a glance"
- Whitepaper on the road to ISO 27001 certification
- ISO/IEC 27001 in Complass: from project brief to certification audit
- Compliance management: catalogs, action plan and evidence
Not legal advice. This guide gives a general overview and does not replace an assessment of the individual case. The wording of your licensed edition of the standard is authoritative. As of November 2026.