

minimum selection TISAX
Start package, size S
€199 net per month
- TISAX: Required by your customers? The framework then covers the requirements. Not a legal duty.
- GDPR, AI Act and Whistleblower protection (HinSchG) (baseline protection)
Framework · TISAX® – preparing for the assessment
Your customer requires a TISAX label? Complass guides you from choosing the labels through the self-assessment under the VDA ISA to the action plan, with all evidence in one place.
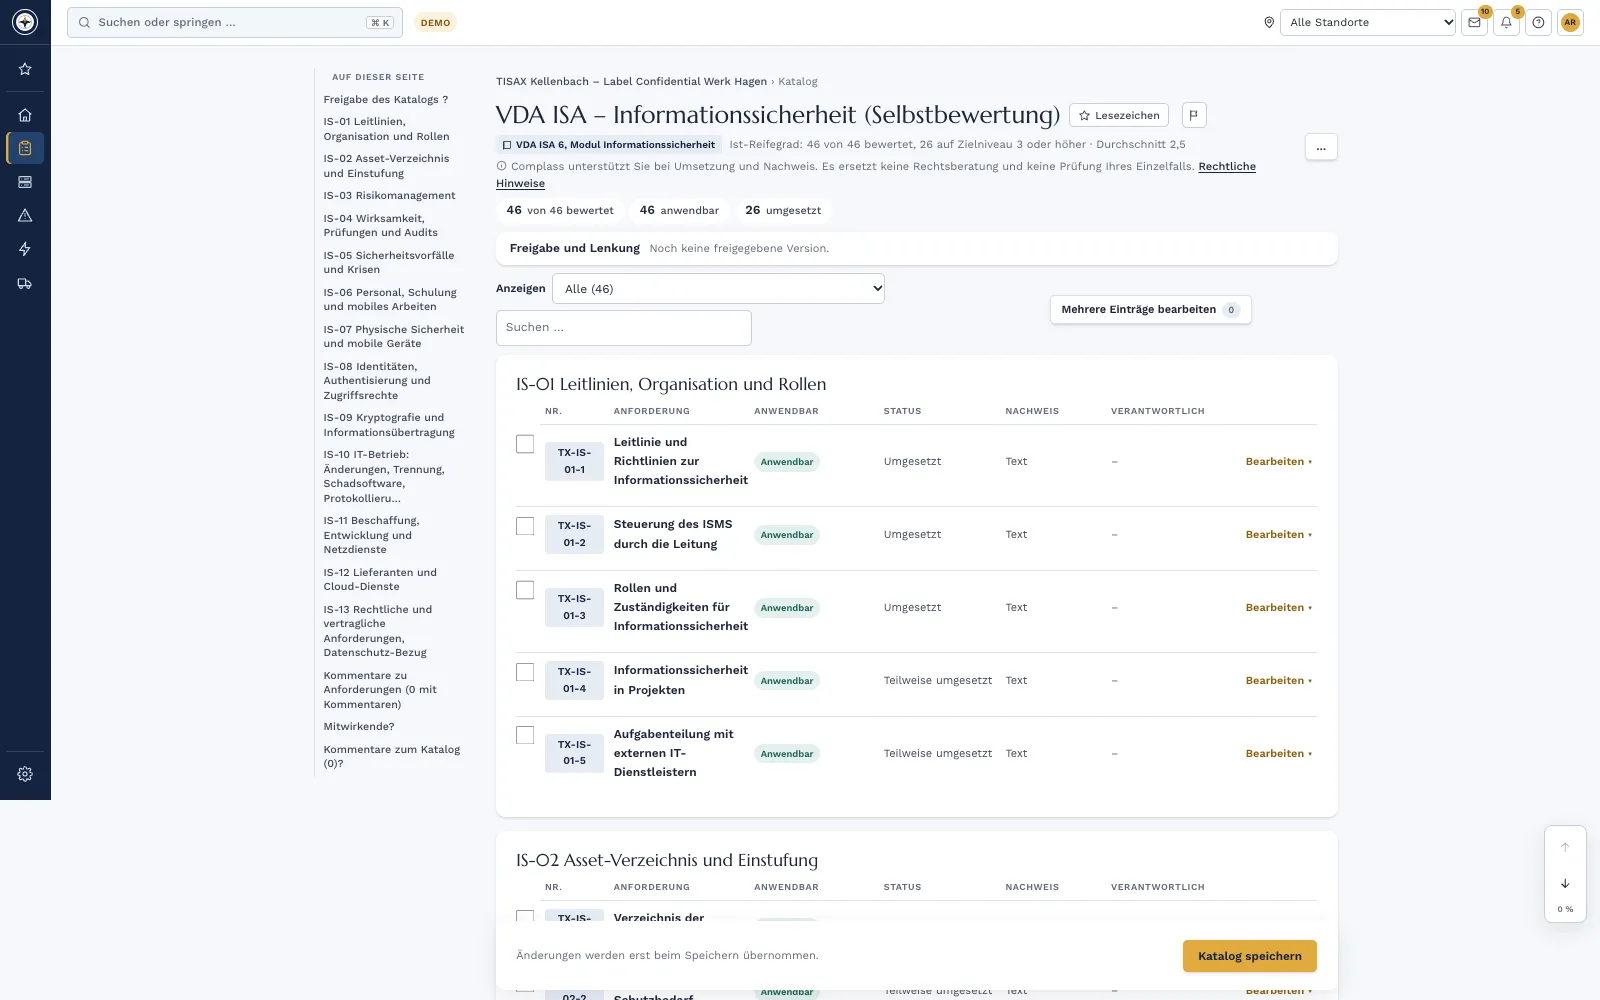
TISAX (Trusted Information Security Assessment Exchange) is the automotive industry’s assessment and exchange mechanism for information security. It is based on the VDA ISA (Information Security Assessment) published by the German Association of the Automotive Industry (VDA). An approved audit provider assesses your company, and you share the result as a label with your customers via the platform of the ENX Association. TISAX is neither a law nor a certificate; it becomes binding through contracts and purchasing conditions.
TISAX® is a registered trademark of the ENX Association. Complass is not affiliated with the ENX Association or the VDA.
Content as of:
TISAX concerns companies that receive confidential information, prototypes or personal data from vehicle manufacturers or large suppliers: parts and system suppliers, engineering service providers, IT and cloud providers, logistics, agencies and test laboratories. The obligation does not arise from a law but from the contract with your customer, who specifies which labels it expects and by when.
Which labels you need depends on what you work with: confidential or strictly confidential information, high availability, prototypes and test vehicles, or data processed on behalf of your customer. In the first phase in Complass you clarify your customer’s requirement and record the target labels.
This overview does not replace legal advice. The legal or normative text is authoritative; in Complass you check applicability with guidance based on the references.
VDA ISA 6 applies to assessments, with today’s objectives for information security and availability
ENX
Test vehicles and events with prototypes are assessed at assessment level 2 (previously level 3)
ENX
VDA ISA 2027 published; from now on a new version every year
ENX
VDA ISA 2027 applies to all assessments ordered from this day; existing labels remain valid
ENX
There are no statutory deadlines for TISAX; your customer sets the schedule. According to ENX, a label is valid for three years from the end of the assessment. Deviations from the initial assessment must be resolved no later than nine months after the closing meeting. In Complass you plan backwards from the customer’s date; you enter the assessment date in the project plan, and the dashboard shows the countdown.
For each requirement you record applicability, current maturity level from 0 to 5, gap and evidence. The VDA ISA number is shown alongside; the description is in our own words. Export to Excel, Word or PDF.
Dedicated phases and catalogues for security areas, test vehicles, events and photo shoots, and for processing on behalf. You only work on them if your customer requires these labels.
Including customer requirement and target labels, assessment scope and sites, prototype protection concept, access and visitors, test vehicles and transport, corrective action plan after the assessment and the policies of your ISMS.
Checklists for the ENX registration, the choice of audit provider and the audit day. You track findings from the assessment in the corrective action plan with owners and deadlines through to the follow-up assessment.
Price: you book TISAX like any other framework. It counts towards the frameworks included in your plan (plans from €199 per month) or is added as a further framework from €99 per month. All prices net plus VAT. To the prices
Training “TISAX basics and implementation” for your team
Catalogue: VDA ISA – Information security (self-assessment)
The assessment level determines how thoroughly the audit provider checks. It follows from the labels your customer requires.
You assess yourself. There is no label and no exchange via ENX. Suitable as a first step and to determine where you stand.
The audit provider checks your self-assessment against evidence and in interviews, usually by video conference. Typical for confidential information, high availability, test vehicles, events with prototypes and data.
On-site assessment with documents, interviews and inspection. Typical for strictly confidential information, very high availability, prototype parts and vehicles and special categories of personal data.
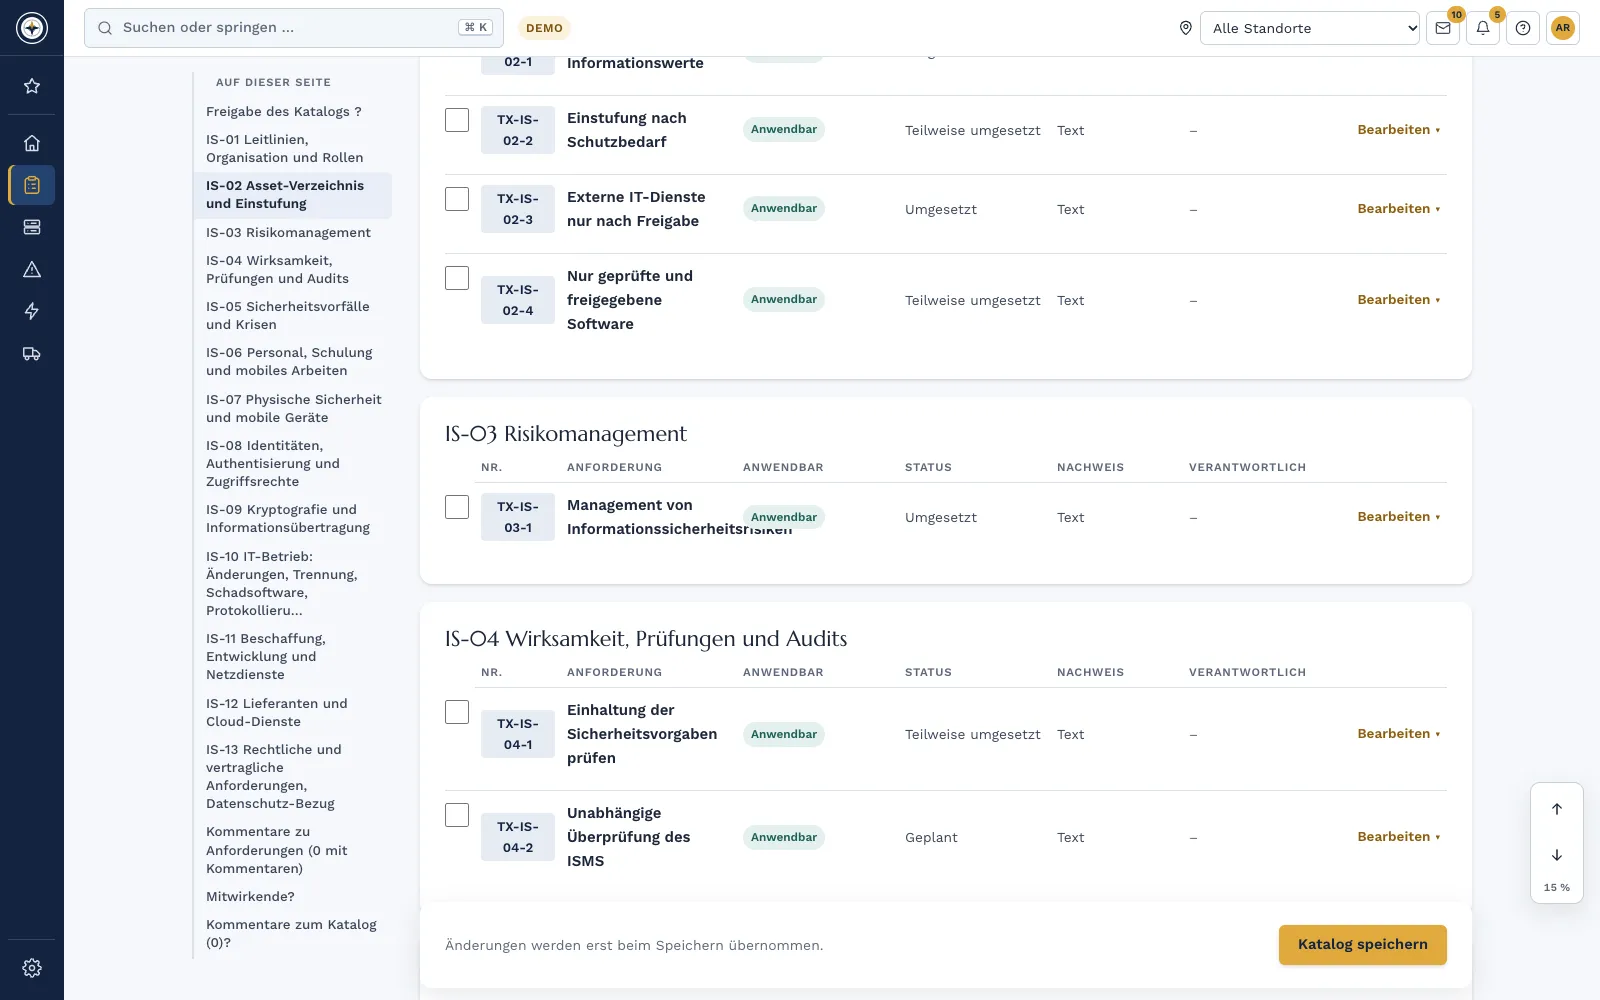
In the self-assessment you record for each requirement how reliably it is implemented. The target is maturity level 3 for every applicable requirement. Complass shows the current maturity level against this target, so you see the gaps at a glance.
Source for labels, levels and target value: ENX TISAX Participant Handbook 2.8. Your customer decides which labels apply to you.
If your customers require TISAX, this selection covers the requirements in Complass.
minimum selection TISAX
€199 net per month
Recommended
€590 net per month
More impact with Asset management and zones, Supplier Management and Business continuity management (BCM), room for 10 users and 2 frameworks.
With annual payment, 12 months minimum term. Monthly payment with a 15 % surcharge. All prices net plus VAT, as of 6 November 2026. All packages and modules in the price overview
You can also meet the requirements without Complass. Complass supports implementation and evidence and does not replace legal advice. Legal information
No. The label requires an assessment by an audit provider approved by ENX, and that assessment decides whether you receive it. Complass prepares you for it: with a self-assessment, the current maturity level per requirement, templates, evidence and a corrective action plan.
No. For each requirement Complass only gives the VDA ISA number and describes it in its own words. You download the official catalogue from ENX and use it alongside; you can store excerpts from it in the project.
No. Registration, ordering the audit provider and sharing the result take place on the ENX portal. Complass prepares the information for it with a checklist.
Yes. The VDA ISA is closely based on ISO/IEC 27001 and 27002, so you will already have implemented many requirements. The policy templates in the TISAX module are structured as in the ISO 27001 module. Prototype protection and data protection are added where needed.
VDA ISA 2027 applies to assessments ordered from 1 January 2027, with partly new numbers. Your answers in Complass are tied to our own stable identifiers and are kept when switching over. The numbers under VDA ISA 2027 are in preparation.
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.