Pilot programme: 30 % off in the first year. Places limited. See the conditions

Book a first call
Complass – Navigate compliance Complass – Navigate compliance

Who it’s for

For industry and mechanical engineering: Production, products and evidence on one line

Monday, 7:40 a.m.

A customer questionnaire asks: who can reach your production through remote maintenance? The answer sits in three spreadsheets and the head of a colleague on vacation.

With Complass it is on one page, with the approval. Your coffee is still warm.

Register of remote maintenance accesses in Complass with supplier, access path, multi-factor sign-in, status and expiry (demo data)

The challenge

Several frameworks at once

NIS2 for the company, the CRA and Machinery Regulation for the products, IEC 62443 for the plants. Each framework brings its own evidence and owners.

Plants nobody knows completely

Controllers from several decades, remote maintenance by vendors and integrators, firmware without support: many plants lack a complete OT inventory.

Customers want evidence

Security questionnaires from customers arrive ever more often, and the answers are scattered across spreadsheets, folders and people’s heads.

What applies to your company

Machine building is listed in Annex 2 of the German BSI Act. From medium size onwards you are therefore an important entity under NIS2, with these obligations:

Frameworks: NIS2 · IEC 62443 · ISO 27001 · Machinery Regulation · CRA · TISAX

  • Machine builders of medium size or larger, usually from 50 employees or more than EUR 10 million in turnover and balance sheet total, fall under NIS2 as important entities Section 28 BSIG and Annex 2§ 28 BSIG Besonders wichtige Einrichtungen und wichtige Einrichtungen(1) Als besonders wichtige Einrichtung gelten - 1. Betreiber kritischer Anlagen, - 2. qualifizierte Vertrauensdiensteanbieter, Top Level Domain Name Registries oder DNS-Diensteanbieter, - 3. Anbieter öffentlich zugänglicher Telekommunikationsdienste oder Betreiber öffentlicher Telekommunikationsnetze, die - a) mindestens 50 Mitarbeiter beschäftigen oder - b) einen Jahresumsatz und eine Jahresbilanzsumme von jeweils …As of: 02.11.2026 · Source: gesetze-im-internet.deOpen original (gesetze-im-internet.de) ↗
  • Implement risk management measures, explicitly also for production plants, remote maintenance and the supply chain § 30 BSIG§ 30 BSIG Risikomanagementmaßnahmen besonders wichtiger Einrichtungen und wichtiger Einrichtungen(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, geeignete, verhältnismäßige und wirksame technische und organisatorische Maßnahmen, die in Absatz 2 konkretisiert werden, zu ergreifen, um Störungen der Verfügbarkeit, Integrität und Vertraulichkeit der informationstechnischen Systeme, Komponenten und Prozesse, die sie für die Erbringung ihrer Dienste nutzen, zu vermeiden und …As of: 02.11.2026 · Source: gesetze-im-internet.deOpen original (gesetze-im-internet.de) ↗
  • Report significant incidents: early warning within 24 hours, notification within 72 hours, final report after one month § 32 BSIG§ 32 BSIG Meldepflichten(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, folgende Informationen an eine vom Bundesamt und dem Bundesamt für Bevölkerungsschutz und Katastrophenhilfe eingerichtete gemeinsame Meldestelle zu melden: - 1. unverzüglich, spätestens jedoch innerhalb von 24 Stunden nach Kenntniserlangung von einem erheblichen Sicherheitsvorfall, eine frühe Erstmeldung, in der angegeben wird, ob der …As of: 02.11.2026 · Source: gesetze-im-internet.deOpen original (gesetze-im-internet.de) ↗
  • The management approves the measures, oversees implementation and regularly attends training § 38 BSIG§ 38 BSIG Umsetzungs-, Überwachungs- und Schulungspflicht für Geschäftsleitungen besonders wichtiger Einrichtungen und wichtiger Einrichtungen(1) Geschäftsleitungen besonders wichtiger Einrichtungen und wichtiger Einrichtungen sind verpflichtet, die von diesen Einrichtungen nach § 30 zu ergreifenden Risikomanagementmaßnahmen umzusetzen und ihre Umsetzung zu überwachen. (2) Geschäftsleitungen, die ihre Pflichten nach Absatz 1 verletzen, haften ihrer Einrichtung für einen schuldhaft verursachten Schaden nach den auf die Rechtsform der Einrichtung …As of: 02.11.2026 · Source: gesetze-im-internet.deOpen original (gesetze-im-internet.de) ↗
  • For your products in addition: CRA reporting obligations and cybersecurity of the control system under the Machinery Regulation Art. 14 CRAArticle 14 Cyber Resilience Act Reporting obligations of manufacturers1. A manufacturer shall notify any actively exploited vulnerability contained in the product with digital elements that it becomes aware of simultaneously to the CSIRT designated as coordinator, in accordance with paragraph 7 of this Article, and to ENISA. The manufacturer shall notify that actively exploited vulnerability via the single reporting platform established pursuant to Article 16. 2. For the purposes of …As of: 06.10.2026 · Source: EUR-Lex – OJ L 2024/2847, 20.11.2024, corrigenda incorporated: OJ L 2024/90780, 5.12.2024; OJ L 2025/90555, 2.7.2025; OJ L 2025/90828, 17.10.2025Open original (EUR-Lex – OJ L 2024/2847, 20.11.2024, corrigenda incorporated: OJ L 2024/90780, 5.12.2024; OJ L 2025/90555, 2.7.2025; OJ L 2025/90828, 17.10.2025) ↗ Annex III 1.1.9 MRAnnex III Section 1.1.9 Machinery Regulation Protection against corruptionThe machinery or related product shall be designed and constructed so that the connection to it of another device, via any feature of the connected device itself or via any remote device that communicates with the machinery or related product does not lead to a hazardous situation. A hardware component transmitting signal or data, relevant for connection or access to software that is critical for the compliance of …As of: 06.10.2026 · Source: EUR-Lex – OJ L 165, 29.6.2023; Art. 3, 8, 20, 25a–25e and 47 as consolidated on 27.07.2026Open original (EUR-Lex – OJ L 165, 29.6.2023; Art. 3, 8, 20, 25a–25e and 47 as consolidated on 27.07.2026) ↗

Typical companies

Special-purpose machinery and plant engineering Focus area

Every plant is a project of its own: zone model and remote maintenance per customer plant, plus your own works under NIS2.

Series machinery and components

Product families with a shared SBOM and vulnerability handling throughout the support period.

Process industry

Chemicals, food and plastics with process control systems: asset inventory, zones and business continuity for production outages.

Automotive suppliers

ISO 27001 as the basis for customer evidence, plus preparation for the TISAX assessment along the VDA ISA.

How Complass helps

OT inventory

Capture controllers without agents

Capture controllers, drives, operator panels and network components from network captures in the browser, with vendor, firmware and end of support.

OT assets with vendor, firmware and end of support in Complass (sample project)

Zones and conduits

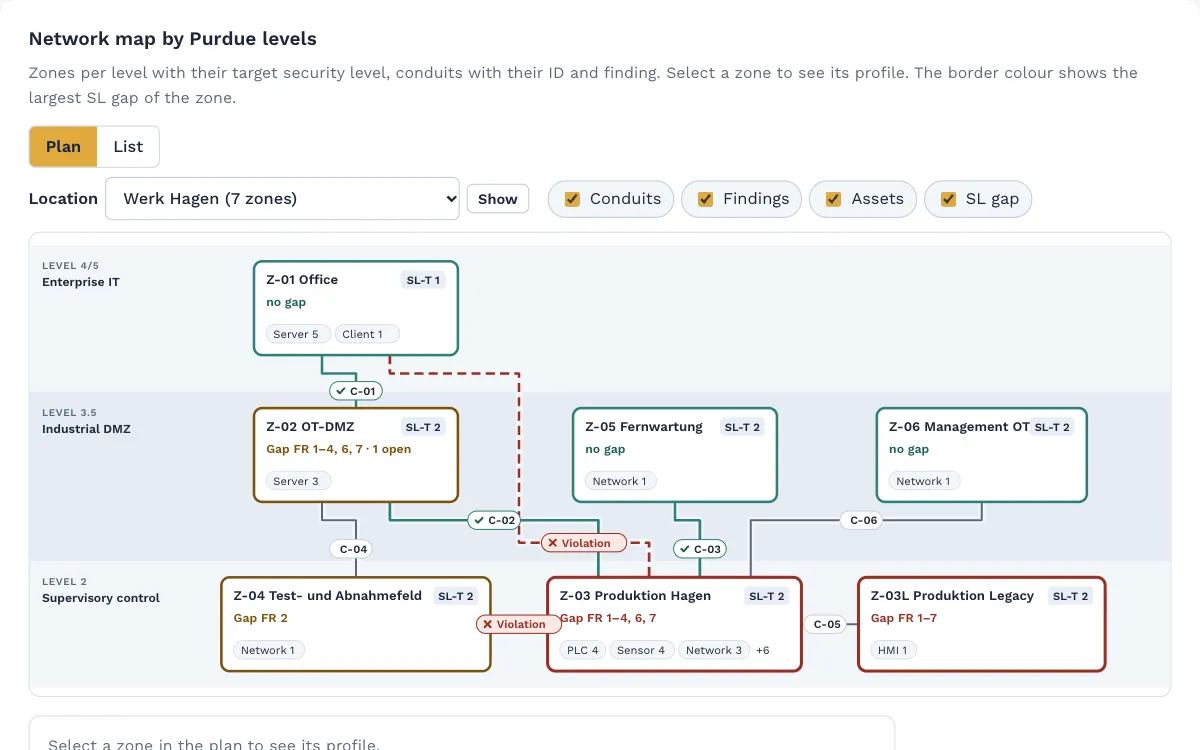
Your production as a plan per IEC 62443

Divide production into zones, document connections and remote access as conduits and set security levels.

Network plan by Purdue levels with the zones and conduits of the demo company

Vulnerabilities

Vulnerabilities by priority

Find known vulnerabilities of your components and rank them by whether they are actively exploited and how exposed the plant is.

Vulnerabilities per asset with priority in Complass (sample project)

You answer your customers’ questionnaires from what you already have and invite your suppliers to a self-assessment.

Matching offers

Two industry templates cover the typical tasks in machine building: one for your own production, one for your own products. They can be combined. For automotive suppliers, TISAX can be added as a framework of its own.

available

Industry template: Industry

  • IEC 62443 for asset owners, integrators and manufacturers
  • Machinery Regulation with the cybersecurity requirements for control systems
  • Asset management for IT and OT
  • MITRE ATT&CK for Enterprise and ICS

from €546 per month plus VAT in the Start package, size S, annual payment

available

Industry template: Manufacturers

  • Cyber Resilience Act per product up to CE marking
  • Radio Equipment Directive with EN 18031
  • Vulnerability management with SBOM

from €447 per month plus VAT in the Start package, size S, annual payment

available

Framework TISAX / VDA ISA

  • Self-assessment along the VDA ISA with maturity levels
  • Preparation for the TISAX assessment
  • Prototype protection and data protection in their own phases

from €199 per month plus VAT in the Start package, size S, annual payment

All prices are for businesses, not for consumers. They are net plus VAT with annual payment; monthly payment carries a surcharge of 15 %. As of 6 November 2026. Enterprise and groups of companies on request.

Frequently asked questions

Do we fall under NIS2 as a machine builder?

If you manufacture machinery and are at least medium-sized, usually yes, as an important entity. What counts is your main activity, the number of employees and turnover and balance sheet total. The applicability check tests this in a few minutes.

Do we need ISO 27001 or IEC 62443?

ISO 27001 is the usual framework for office IT and the management system, IEC 62443 for production and plants. Many industrial companies use both. In Complass you link the requirements so that you document a measure only once.

Our customers send us more and more security questionnaires. Does Complass help with that?

Yes. Your measures, evidence and documents are kept in one place and can be prepared for customers as Excel or PDF. This way you answer recurring questions from what you already have.

Try Complass with your own data

Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.