

Framework · Energy Industry Act (EnWG) and IT security catalogue
Implement EnWG IT security catalogue step by step
Applies in Germany only (German law). For network and energy plant operators under §§ 5c to 5e EnWG: Complass guides you from clarifying your role through the IT security catalogue to incident reporting and evidence.

What is the IT security catalogue under the EnWG?
Applies in Germany only (German law). Since 6 December 2025, sections 5c to 5e of the German Energy Industry Act (EnWG) govern IT security in the energy sector. What operators must implement in detail is set by the Federal Network Agency (BNetzA), in agreement with the BSI, in an IT security catalogue. The act names twelve topics that every catalogue must contain at least, from risk analysis through attack detection to multi-factor authentication. In addition there are the reporting of significant security incidents, registration, documentation and the responsibility of management.
Content as of:
Does it apply to me?
The EnWG distinguishes three roles. For network operators it applies regardless of size; operators of energy facilities and digital energy services are covered if they are important or particularly important entities under the German BSI Act.
| Role | Covered if | What applies today |
|---|---|---|
| Electricity or gas network operators | You operate an energy supply network, no size threshold | IT security catalogue for network operators, August 2015 |
| Operators of energy facilities, e.g. generation or storage | Energy facility connected to the network and important or particularly important entity under section 28 BSIG | IT security catalogue for energy facilities, December 2018 |
| Digital energy services, e.g. aggregators | Service on an energy facility connected to the network and important or particularly important entity under section 28 BSIG | No BNetzA catalogue yet. Aggregators formerly covered by section 8a BSIG (old version) continue to implement the BDEW “B3S Aggregatoren”. |
Entities subject to sections 5c to 5e EnWG are exempt from most duties of the BSI Act; classification and registration remain. If municipal utilities also run water, waste water or other lines of business from Annex 1 or 2 of the BSI Act (multi-utility), the BSI Act applies to them. In Complass you manage these lines of business in a NIS2 project and link shared evidence. Telecommunications services are governed by the Telecommunications Act (TKG).
This overview does not replace legal advice. The legal or normative text is authoritative; in Complass you check applicability with guidance based on the references.
Legal basis
- § 5c EnWG§ 5c EnWG IT-Sicherheit im Anlagen- und im Netzbetrieb, Festlegungskompetenz(1) Die folgenden Betreiber haben für die genannten Systeme einen angemessenen Schutz gegen Bedrohungen zu gewährleisten: - 1. der Betreiber eines Energieversorgungsnetzes für Telekommunikationssysteme und für elektronische Datenverarbeitungssysteme, die für den sicheren Betrieb des Energieversorgungsnetzes notwendig sind, - 2. der Betreiber einer Energieanlage, der eine besonders wichtige Einrichtung nach § 28 …Open original (gesetze-im-internet.de) ↗IT security, roles, catalogue and its twelve minimum topics
- § 5d EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗Documentation, contact person, reporting and registration
- § 5e EnWG§ 5e EnWG Umsetzungs-, Überwachungs- und Schulungspflicht für Geschäftsleitungen(1) Die Geschäftsleitung eines Betreibers nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 ist verpflichtet, die Anforderungen des IT-Sicherheitskatalogs umzusetzen und die Umsetzung zu überwachen. (2) Eine Geschäftsleitung eines Betreibers nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3, die ihre Pflichten nach Absatz 1 verletzt, haftet ihrer Einrichtung für einen schuldhaft verursachten Schaden nach den auf die Rechtsform der …Open original (gesetze-im-internet.de) ↗Duties of management
- § 28 BSIG§ 28 BSIG Besonders wichtige Einrichtungen und wichtige Einrichtungen(1) Als besonders wichtige Einrichtung gelten - 1. Betreiber kritischer Anlagen, - 2. qualifizierte Vertrauensdiensteanbieter, Top Level Domain Name Registries oder DNS-Diensteanbieter, - 3. Anbieter öffentlich zugänglicher Telekommunikationsdienste oder Betreiber öffentlicher Telekommunikationsnetze, die - a) mindestens 50 Mitarbeiter beschäftigen oder - b) einen Jahresumsatz und eine Jahresbilanzsumme von jeweils …Open original (gesetze-im-internet.de) ↗Classification as an important or particularly important entity, exemption under subsection 5
- § 32 BSIG§ 32 BSIG Meldepflichten(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, folgende Informationen an eine vom Bundesamt und dem Bundesamt für Bevölkerungsschutz und Katastrophenhilfe eingerichtete gemeinsame Meldestelle zu melden: - 1. unverzüglich, spätestens jedoch innerhalb von 24 Stunden nach Kenntniserlangung von einem erheblichen Sicherheitsvorfall, eine frühe Erstmeldung, in der angegeben wird, ob der …Open original (gesetze-im-internet.de) ↗Reporting obligations and deadlines
- Section 11(1a) and (1b) EnWG, old versionBasis of the two catalogues in force (2015 and 2018)
What applies today and what may come in 2027
-
Sections 5c to 5e EnWG in force (NIS2 Implementation Act). Section 11(1a) to (1g) EnWG, old version, no longer apply.
-
Deadline for registration with the BSI for network operators that are not important or particularly important entities
§ 5d Abs. 4 EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗
-
Today
Until a new catalogue is published, the catalogues of August 2015 (networks) and December 2018 (energy facilities) remain in force. Existing attack detection systems must continue to be operated. Checked on 2 November 2026.
-
End of October 2026
After a two-year transition, the new edition ISO/IEC 27019:2024 (published on 18 October 2024) is the basis for audits under the conformity assessment programme of the Federal Network Agency.
-
24 hours / 72 hours / one month
Significant security incidents to the BSI reporting office: early warning, incident notification, final report
§ 5d Abs. 3 EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗ with § 32 BSIG§ 32 BSIG Meldepflichten(1) Besonders wichtige Einrichtungen und wichtige Einrichtungen sind verpflichtet, folgende Informationen an eine vom Bundesamt und dem Bundesamt für Bevölkerungsschutz und Katastrophenhilfe eingerichtete gemeinsame Meldestelle zu melden: - 1. unverzüglich, spätestens jedoch innerhalb von 24 Stunden nach Kenntniserlangung von einem erheblichen Sicherheitsvorfall, eine frühe Erstmeldung, in der angegeben wird, ob der …Open original (gesetze-im-internet.de) ↗
-
Without undue delay
Submit the documentation to the Federal Network Agency: network operators always, operators of energy facilities and digital energy services as particularly important entities (professional assessment, not legal advice)
§ 5d Abs. 1 Satz 2 EnWG§ 5d EnWG Dokumentations-, Melde-, Registrierungspflicht(1) Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 bis 3 hat die Einhaltung der Anforderungen des IT-Sicherheitskatalogs zu dokumentieren. Der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 1 und der Betreiber nach § 5c Absatz 1 Satz 1 Nummer 2 und 3, der jeweils eine besonders wichtige Einrichtung nach § 28 Absatz 1 des BSI-Gesetzes ist, hat die Dokumentation nach Satz 1 der Bundesnetzagentur unverzüglich nach der …Open original (gesetze-im-internet.de) ↗
-
Autumn 2026
Consultation on a joint catalogue for networks, energy facilities and digital energy services, planned according to the Federal Network Agency
-
1 January 2027 (unconfirmed draft date)
Start of application cited in specialist articles from a draft. The new catalogue has not been fixed yet; the Federal Network Agency has not confirmed this date and names none on its procedure page.
We check the status at the Federal Network Agency before every release. When a new catalogue is fixed, Complass adds it as a new edition; your assessments of the twelve topics are kept.
How Complass helps
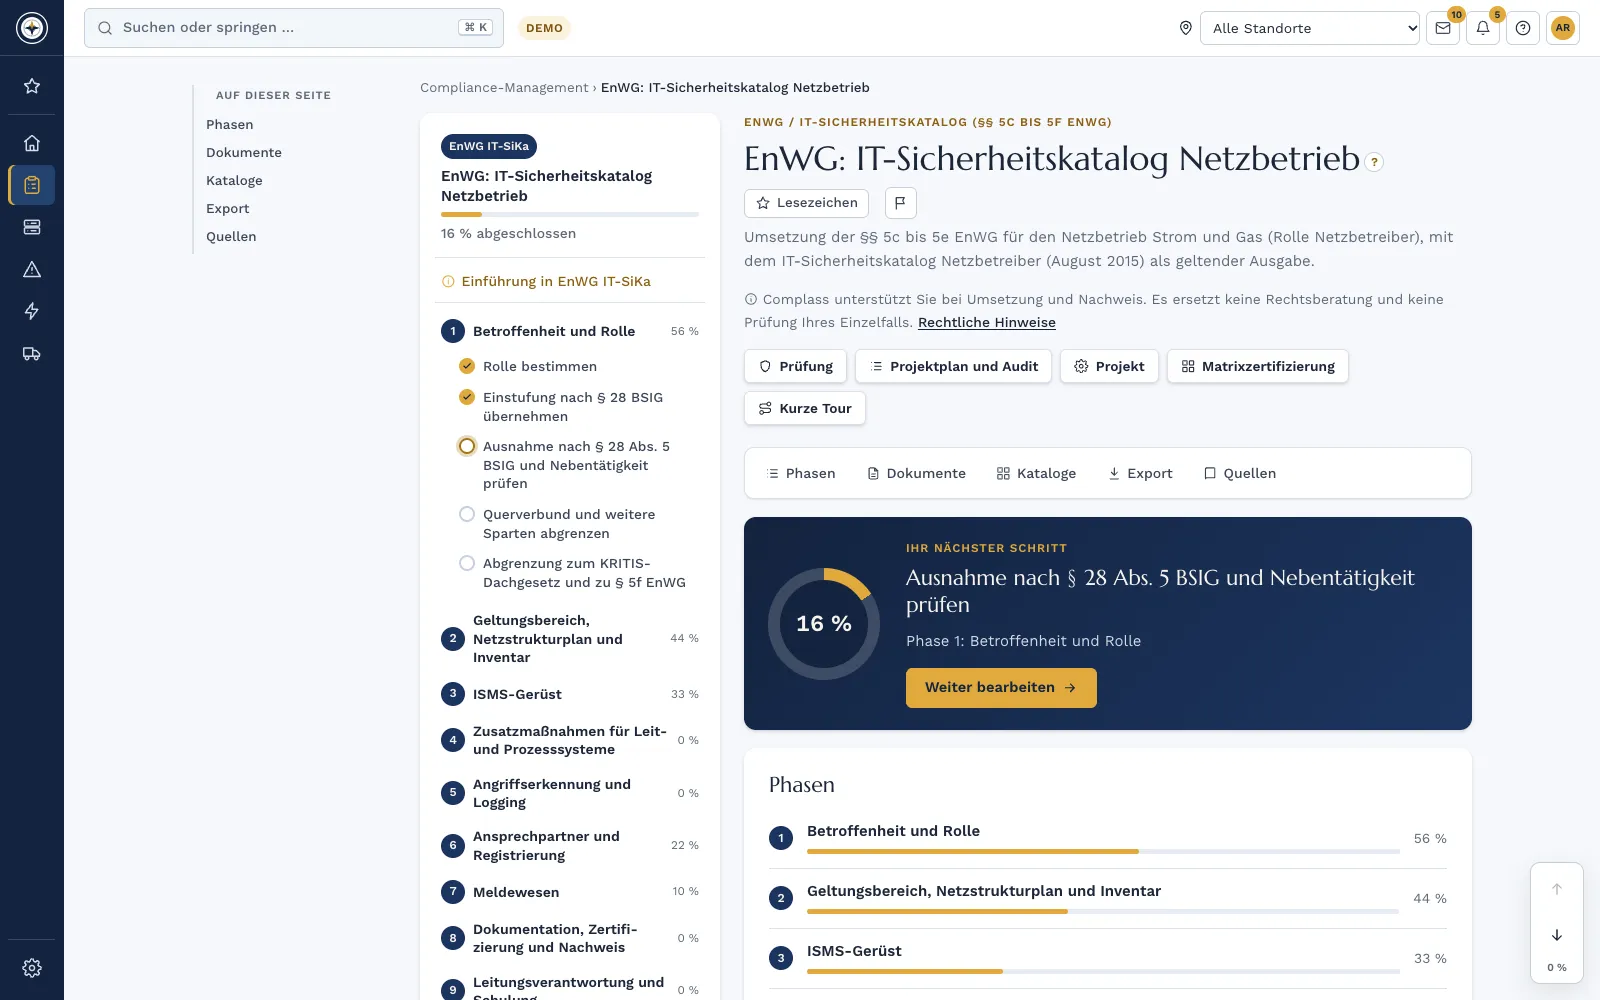
- 10phases
- 30guided steps
- 8document templates
- 77requirements in the catalogue
Twelve topics that stay
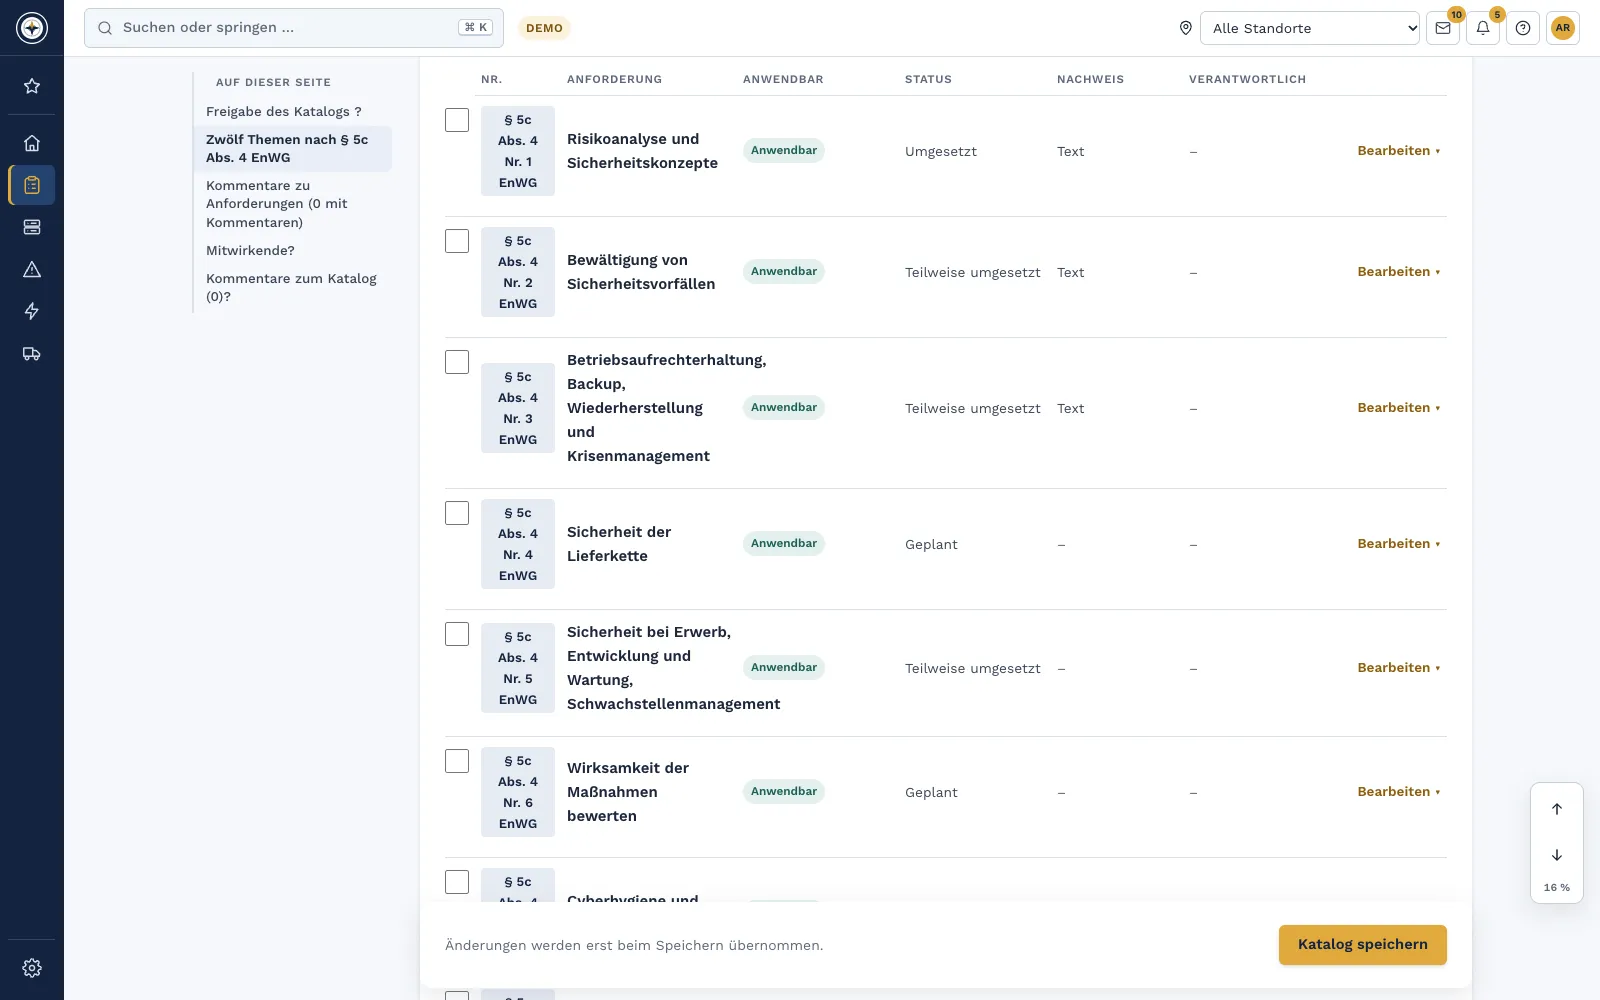
You assess the twelve topics of section 5c(4) EnWG once. The requirements of the 2015 and 2018 catalogues are linked to them. When the new catalogue comes, Complass adds it as a new edition without you having to start over.
The catalogue that applies to your role
Network operators work with the 2015 catalogue, operators of energy facilities with the 2018 catalogue, each with the requirements in their original wording and the source. Digital energy services use the twelve topics as their basis.
Network structure plan, inventory and control systems
Scope, network structure plan and systems in asset management, zones and remote access for control and process systems.
Attack detection and logging
Concept for attack detection systems with monitored systems, responsibilities and response to alerts.
Reports to the BSI reporting office
Reporting process with the deadlines of 24 hours, 72 hours and one month and distinction from reports under the KRITIS Umbrella Act. You record incidents in incident management with the time of awareness; if you have also booked NIS2, Complass calculates the reporting deadlines.
Multi-utility with NIS2 in one portal
You manage further lines of business in the NIS2 project. You link shared evidence instead of maintaining it twice.
Management and training
Management duties under section 5e EnWG with learning blocks for specialists and for management.
The phases in the module
- Applicability and role
- Scope, network structure plan and inventory
- ISMS skeleton
- Additional measures for control and process systems
- Attack detection and logging
- Contact person and registration
- Incident reporting
- Documentation, certification and evidence
- Management responsibility and training
- Supply chain and critical functions
Catalogue: Minimum contents of the IT security catalogue (section 5c(4) EnWG)
Frequently asked questions
Does the EnWG or the BSI Act apply to us?
For network operation and for energy facilities of important or particularly important entities, sections 5c to 5e EnWG apply; most duties of the BSI Act do not apply to them. Classification and registration under the BSI Act remain. Further lines of business such as water or waste water are subject to the BSI Act. If the energy facility is only a secondary activity in relation to the business as a whole, the BSI Act applies as well.
Which IT security catalogue applies at the moment?
For network operators the catalogue of August 2015, for operators of energy facilities the catalogue of December 2018. According to the Federal Network Agency, both remain in force until a new catalogue is published. Status checked: 2 November 2026.
What changes with the new catalogue?
The Federal Network Agency, together with the BSI, is revising the catalogues into one catalogue that is also to apply to digital energy services. Specialist articles cite 1 January 2027 from a draft as the start of application; the Federal Network Agency has not confirmed this date. Nothing has been fixed yet. Your work on the twelve topics of section 5c(4) EnWG counts in any case, because every catalogue must contain them.
We are an aggregator. What do we do until the new catalogue?
If you were previously covered by section 8a BSIG (old version), continue to implement the BDEW “B3S Aggregatoren”. Otherwise build an ISMS under ISO/IEC 27001 and orient yourself by the twelve topics. In Complass you assess these topics and add the new catalogue as soon as it is fixed.
To whom do we report a security incident?
To the BSI reporting office: an early warning within 24 hours, an incident notification within 72 hours and a final report one month later at the latest. If the incident is relevant to the security of energy supply, the BSI forwards the report to the Federal Network Agency (section 5d(5) EnWG).
Does Complass replace a legal review?
No. Complass structures the applicability check, obligations and evidence based on the legal text and the catalogues; the legal assessment of the individual case remains with you.
Does NIS2 apply to your company as well?
The free applicability check assesses in a few minutes whether you are covered by the German BSI Act (NIS2), for example with lines of business such as water or district heating. It does not assess whether sections 5c to 5e EnWG apply: for network operators they apply regardless of size, for operators of energy facilities and digital energy services once they are classified as important or particularly important entities.
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.