

Productcompliance
Productcompliance: Eén dossier per product in plaats van vijf mappen
Vrijdag, 16:10 uur
A customer asks whether your controller contains a certain library. Engineering searches, sales writes the third email.
In Complass you open the version. The answer is a file, not an email thread.

The CE cyber file: one place per product and version
Requirements, documents, SBOM and status belong together. So in Complass they sit together, for each version separately.
Create
Product and version, CRA class, support period and conformity procedure.
Beoordelen
Every requirement of CRA Annex I and Machinery Regulation Annex III with status and reason.
Generate
Technical documentation, risk assessment, user information and EU declaration of conformity, in German or English.
Declare
Complass shows what is still missing. You sign the declaration.
New version, same work? No. You copy the assessments of the previous version and change what has changed.
You see what is missing in the document. A gap appears there as “[missing: …]” instead of going unnoticed.
An authority asks? The documents of the version are built as one encrypted ZIP with checksums.
SBOM
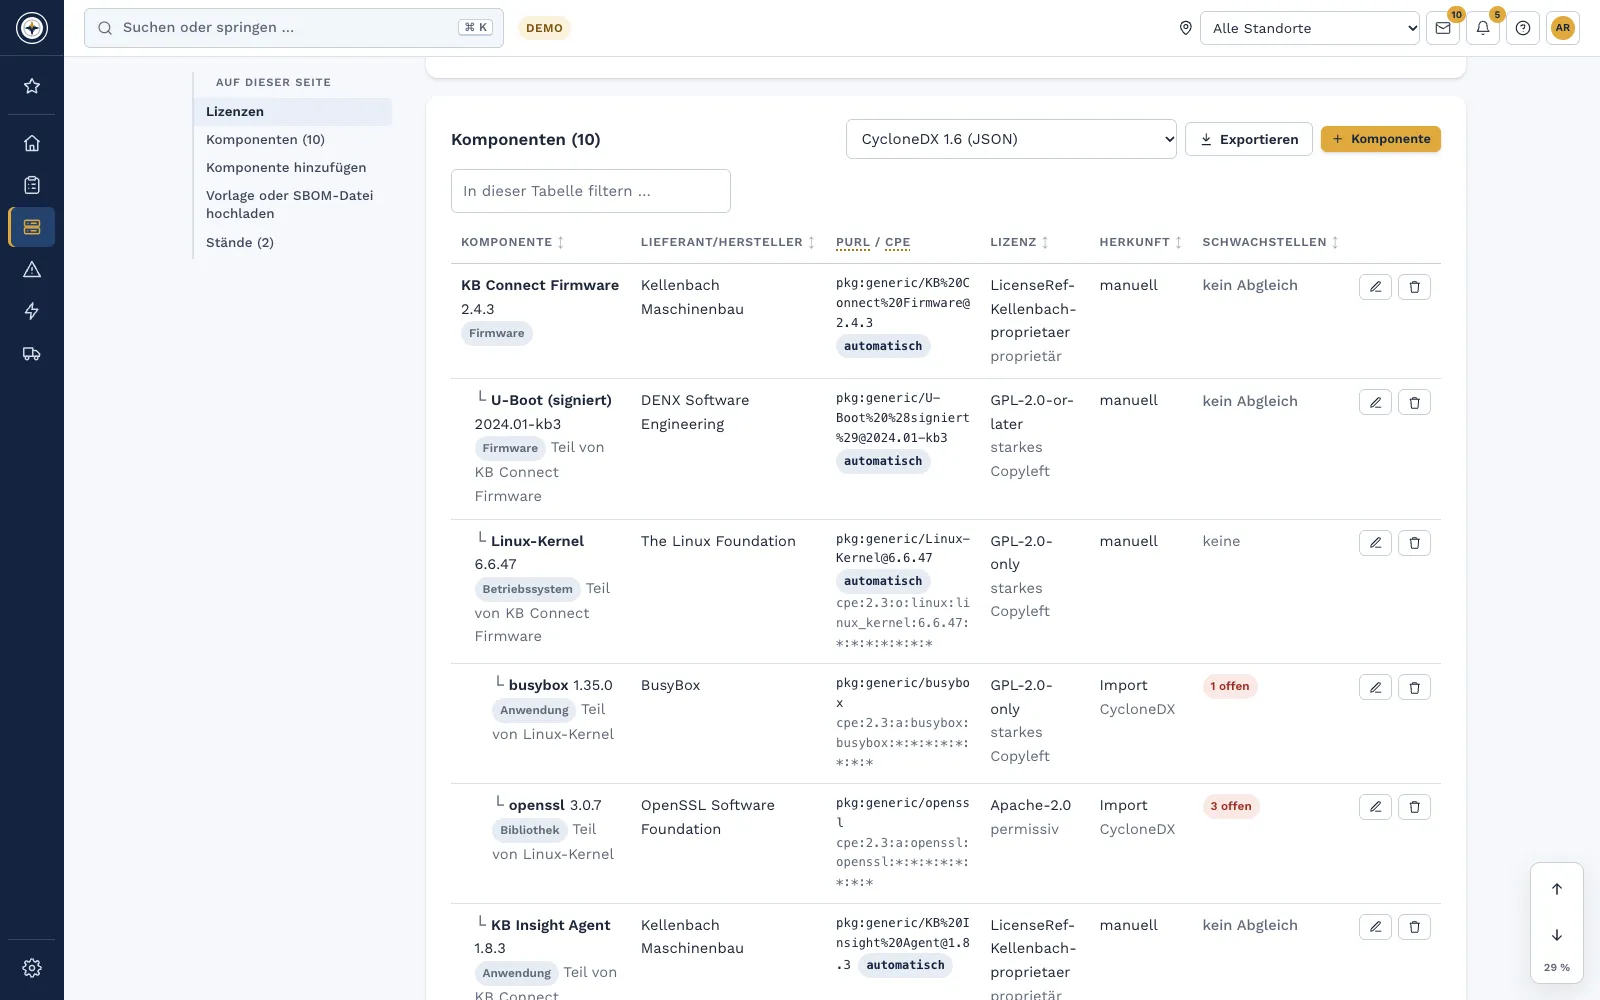
The SBOM belongs to the version, not the inbox
You import CycloneDX or SPDX or let the SBOM arrive from GitLab. Complass keeps comparing the components with public vulnerability data and shows findings per component.
CSAF and VEX
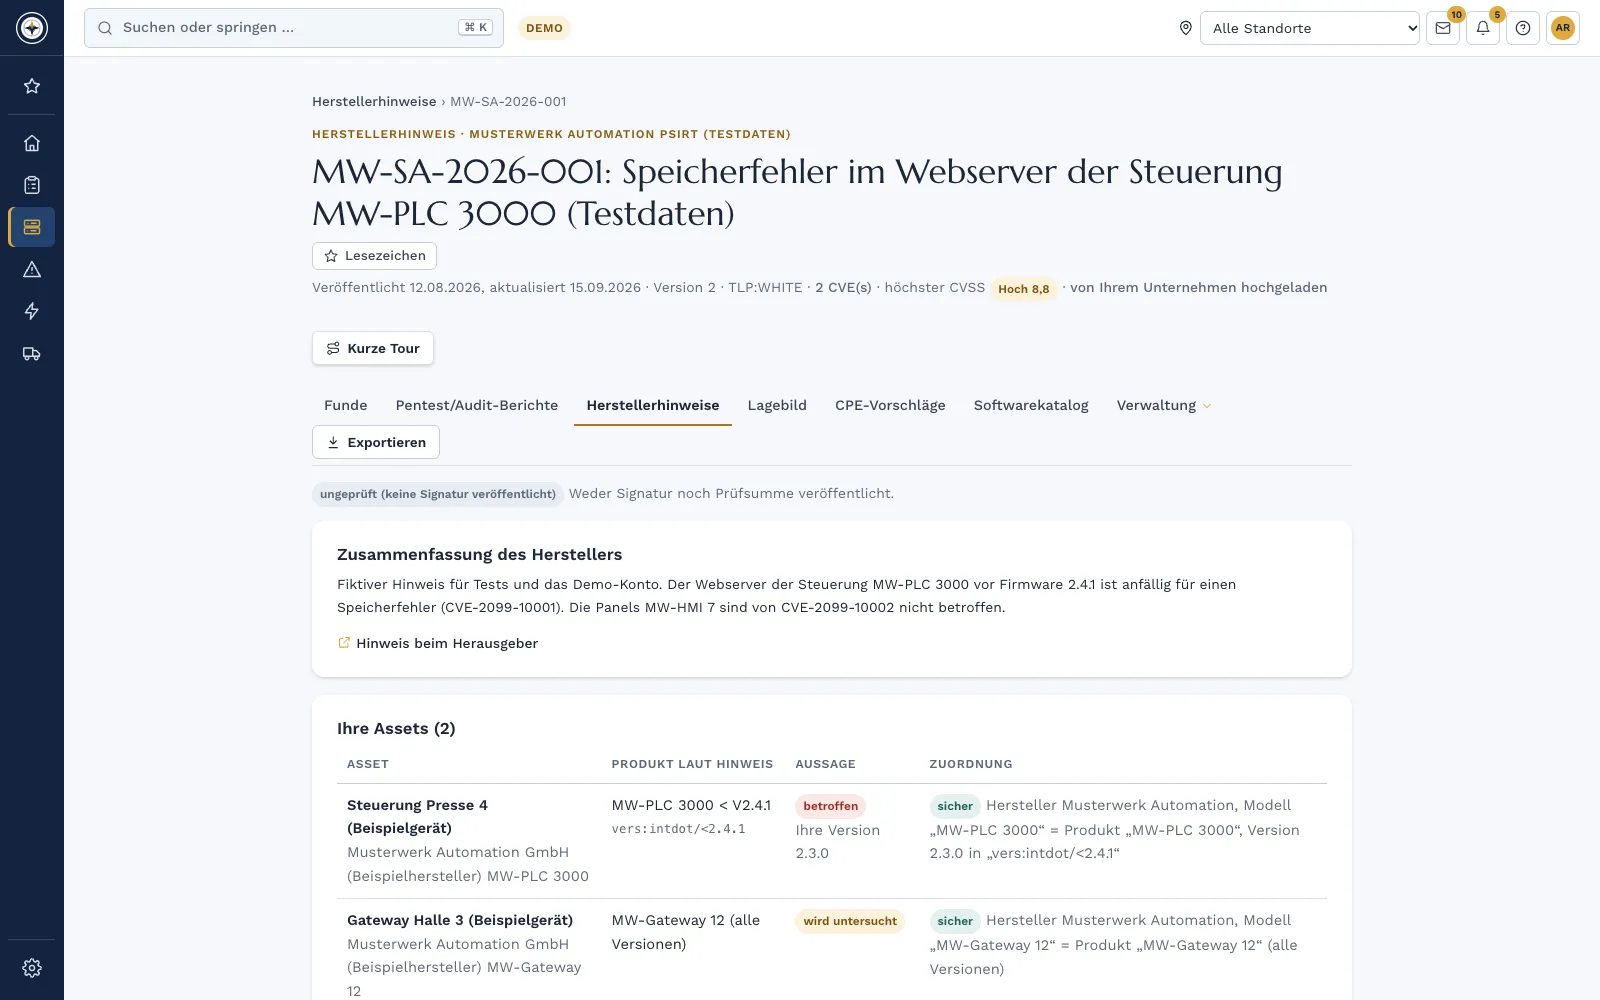
Security advisories as CSAF, not as a mass email
You write the advisory once. Complass turns it into a CSAF 2.0 document, publishes it with a feed and sends it to your lists, with proof of dispatch. Whether a finding affects your product, you state as VEX. Complass reads your suppliers’ advisories in the same format and shows the assets affected.
Reports from outside arrive through your public report form, no sign-in needed. From acknowledgment to publication they stay in one flow, and Complass also generates your security.txt and disclosure policy.
Your customers fetch the current state themselves
No more SBOMs as attachments. You release a version, and your customers find it in their Complass account.
You release
SBOM, VEX or security advisory, as an unchangeable version with a checksum.
Your customer takes it over
They view, download or import the version and hear about new releases.
You see the status
The date per customer: viewed, downloaded, imported.
Assets, internal notes, names of people and other recipients do not leave your account in the process.
CRA and Machinery Regulation, side by side per product
You use many documents for both. Complass keeps the frameworks per product and assigns your reporting cases to the version.
- Cyber Resilience Act
One project per product, from applicability to the declaration of conformity.
- Machineverordening
Protection against corruption and safety of the control system, in the same file.
- IEC 62443 voor fabrikanten
Secure development per 4-1 and components per 4-2, linked with the CRA.
- Complass voor fabrikanten
Duties, bundle and sectors at a glance.
Veelgestelde vragen
Does Complass declare conformity for us?
No. The completeness check shows whether requirements, support period, SBOM and documents are in place. It does not assess conformity and never sets the status “declared”. That stays your decision as the manufacturer.
Which SBOM formats does Complass accept?
CycloneDX 1.4 to 1.6 as JSON or XML and SPDX 2.2 and 2.3. Plus spreadsheets or CSV and entry by hand. You can export as CycloneDX and SPDX.
We are an importer or distributor. Does this suit us too?
Yes. You create the product with your role and file the manufacturer’s declaration. The page for importers and distributors has more on this.
Do our customers need a Complass account?
For the exchange in the portal, yes. Anyone can reach your public security advisories and the CSAF feed without an account.
A file that grows with the product
In the demo we show you the CE cyber file, SBOM and security advisories on a sample product and work out what suits your products.