

Risk assessment template
Risk matrix template (5×5) based on ISO 27005
A matrix of likelihood and impact with described levels, risk classes, acceptance rules and a risk register to fill in.
What the file contains
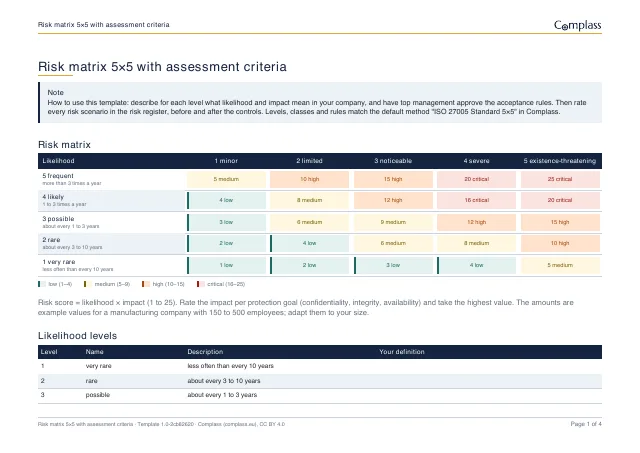
A matrix with five levels of likelihood and impact, each level with a description and example amounts. Plus four risk classes with their score range, who may accept which class, how often you review, and an empty risk register.
| Likelihood ↓ impact → | Impact 1 minor | Impact 2 limited | Impact 3 noticeable | Impact 4 severe | Impact 5 existence-threatening |
|---|---|---|---|---|---|
| 5 frequent | 5 medium | 10 high | 15 high | 20 critical | 25 critical |
| 4 likely | 4 low | 8 medium | 12 high | 16 critical | 20 critical |
| 3 possible | 3 low | 6 medium | 9 medium | 12 high | 15 high |
| 2 rare | 2 low | 4 low | 6 medium | 8 medium | 10 high |
| 1 very rare | 1 low | 2 low | 3 low | 4 low | 5 medium |
- low: score 1 to 4, may be accepted by: Risk owner with a justification
- medium: score 5 to 9, may be accepted by: Risk owner with a justification
- high: score 10 to 15, may be accepted by: Top management, with a justification and for a limited time
- critical: score 16 to 25, may be accepted by: not acceptable, treatment required
Template version 1.0-2cb82620 · content as of 26 September 2026 · Excel (XLSX) 53 KB · PDF 24 KB
This template exists in German and English; you get the English version.
This template is not legal advice. It does not replace checking which requirements apply to your company and does not guarantee any audit or certification result. License CC BY 4.0
How to use the file
Describe the levels
Adapt the descriptions and amounts to your company. A method is good when two people reach the same result.
Approve acceptance
Top management approves the classes and acceptance rules. Clause 6.1.2 of ISO/IEC 27001 asks for defined acceptance criteria.
Rate the risks
For each scenario in the register, enter likelihood and impact before and after the controls. The score is the product of both levels.
The portal takes it from there
The matrix matches the default method "ISO 27005 Standard 5×5" in Complass. There you adapt levels, classes and acceptance rules, and every save is a new version. Each risk gets an inherent, a residual and a target rating, and acceptance runs with a justification, an expiry date and a review reminder.
Preguntas frecuentes
Is a 5×5 matrix mandatory?
No. ISO/IEC 27001 prescribes no matrix; it asks for a method with defined criteria that gives comparable results. A 4×4 matrix with well-described levels is often enough too.
Is ISO 27005 mandatory for certification?
No. The audit checks the requirements of ISO/IEC 27001, and you choose the method. ISO/IEC 27005 is widely used guidance for it.
What do the amounts in the template mean?
They are example values for a manufacturing company with 150 to 500 employees. Use values that fit your size.
How often do we rate the risks again?
ISO/IEC 27001 asks for it at planned intervals and after significant changes (clause 8.2). The template suggests an interval per class, from three months to two years.
Pruebe Complass con sus propios datos
Cree usted mismo su acceso de prueba, con un proyecto de ejemplo por marco normativo si lo desea. Si prefiere que primero le mostremos Complass, solicite una demo.