


This guide shows what each framework asks for, which details you need and how to connect register and record so that both stay current. The examples are invented.
What ISO 27001 and the GDPR each require
ISO/IEC 27001:2022 requires an inventory of information and other associated assets, including their owners, in Annex A.5.9. The neighboring controls build on it: A.5.10 covers acceptable use, A.5.12 the classification of information and A.5.13 its labeling. If you aim for certification, you show the auditor a maintained list with owners and a classification.
The GDPR does not speak of assets. Art. 30(1) GDPR requires a record of processing activities with purposes, categories of data subjects and personal data, recipients, third-country transfers and, where possible, erasure periods and a general description of the technical and organizational measures (TOMs) under Art. 32(1) GDPR. Art. 32(1)(b) GDPR names the confidentiality, integrity, availability and resilience of processing systems and services. You can only describe those measures if you know which systems a processing activity runs on.
The BSI (German Federal Office for Information Security) takes the same route in IT-Grundschutz: the structure analysis under BSI Standard 200-2 records business processes, applications, IT systems, rooms and connections, and the determination of protection requirements places them in the categories normal, high and very high.
The common ground is plain: both sides need the same systems, only from a different angle. The ISMS asks: which assets do we have, and how important are they? Data protection asks: which processing runs where, and how is it protected?
Why two lists do not work
In many companies IT keeps a spreadsheet of systems, while the data protection officer keeps a record in a Word file. Both are created separately, and both go out of date separately.
- Contradictions: The record says "personnel file on the file server", but IT moved the file to a cloud application long ago.
- Double work: A new system is entered twice, with two owners and two classifications.
- Gaps in incidents: When a server fails or is attacked, data protection asks which processing activities are affected. Without a link, the search starts by email.
- TOMs without context: The TOM list describes measures nobody can assign to a specific system.
One register, two views: how to build it
- Set the scope. Follow the scope of your ISMS: sites, departments, service providers.
- Record systems and services. Servers, workstations, network components, business applications and cloud services. In production, controllers, operator stations and terminals belong in it too.
- Name the owners. Every asset gets a responsible person or department, not "IT".
- Rate the protection requirements. Confidentiality, integrity and availability, each normal, high or very high. A system inherits at least the protection requirements of the data it processes.
- Link processing activities. Every activity in the record refers to the assets it runs on, instead of naming systems as free text.
- Assign the TOMs. Describe the TOMs once and refer to the ISMS controls that implement them.
- Tie upkeep to change. Every introduction, change or shutdown of a system updates the register, and the record follows through the link.
Which detail goes where
| Detail | Asset register (ISO 27001) | Record (Art. 30 GDPR) |
|---|---|---|
| Name and type | Yes, unique | Reference to the asset |
| Responsible person or department | Yes (A.5.9) | Responsibility for the activity |
| Protection requirements (confidentiality, integrity, availability) | Yes | Basis for the TOMs |
| Purpose and legal basis | No | Yes |
| Categories of data subjects and data | A "personal data" flag is enough | Yes |
| Recipients and third countries | Service location, provider | Yes |
| Erasure periods | No | Yes, where possible |
| Technical and organizational measures | ISMS controls | General description, reference to the ISMS |
The table shows the division of labor: the register describes the technology, the record describes the processing. The reference connects them.
Example from mechanical engineering
The example is invented. A machine builder with 180 employees is preparing for ISO 27001 certification. IT has a list of 140 entries, and the data protection officer's record has 23 activities.
- Comparison: The activity "time recording" only names "time recording system". In fact, data flows through six terminals on the shop floor, a server and the vendor's cloud application. None of the terminals was on the IT list, because maintenance looks after them.
- Protection requirements: The activity "payroll" processes health data (sick notes). Its cloud application was rated "normal" in the register and is raised to "high" for confidentiality.
- Result: One register with 152 assets, and every activity refers to its systems. When the time recording server fails, data protection sees at once which activities are affected.
Classification without overdoing it
Many registers fail because of too many levels. Three levels per protection goal are enough for most companies, and they match the BSI method. Clear rules matter more than the number of levels:
- Written criteria: When is confidentiality "high"? For example for special categories under Art. 9 GDPR, trade secrets or customers' design data.
- Inheritance: A system takes on the highest protection requirements of the information it processes.
- Labeling: What is classified is also made recognizable under A.5.13, for example in the document header.
Checklist
- The scope of the register matches the scope of the ISMS.
- Systems, applications and cloud services are recorded, in production as well.
- Every asset has a responsible person or department.
- Confidentiality, integrity and availability are rated against written criteria.
- Every processing activity refers to its assets.
- The TOMs refer to the ISMS controls.
- New, changed and decommissioned systems update the register as a binding step.
- Register and record each have a confirmed review date.
Register and record in Complass
Reconciling two spreadsheets by email costs days every year. In Complass both sides are connected:
- Inventory: You take over existing Excel and CSV lists. Every asset has a type, an owner and protection requirements for confidentiality, integrity and availability at the levels normal, high and very high. The overview shows how many assets still have no owner.
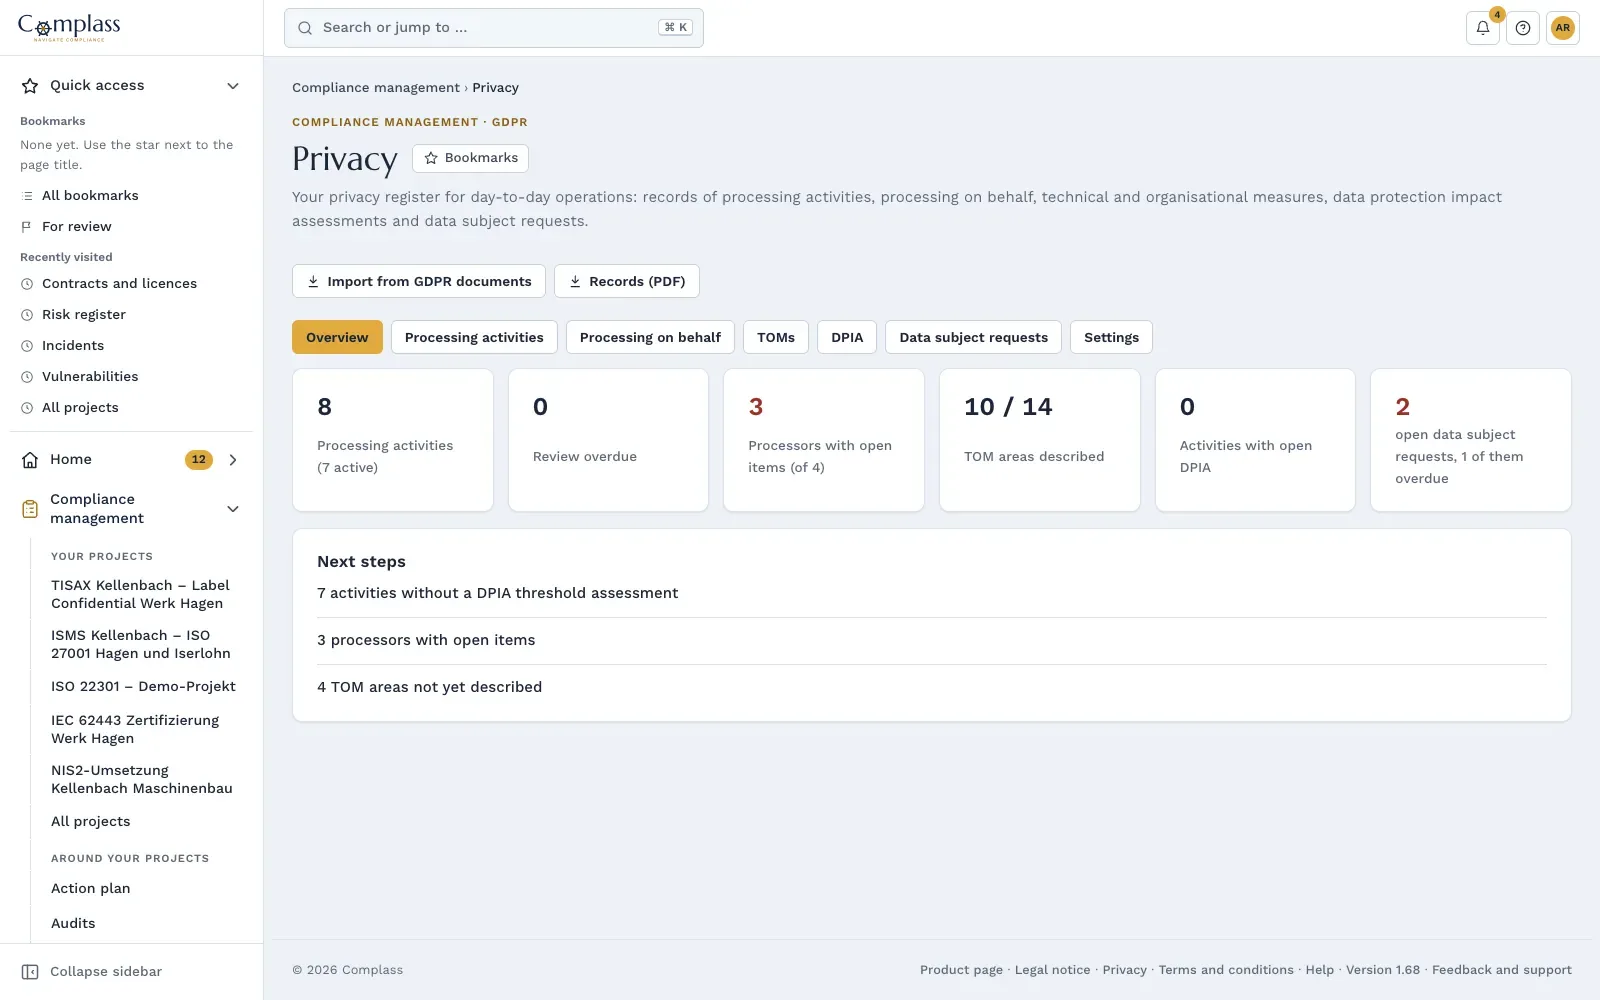
- Record: The record of processing activities holds the details under Art. 30 GDPR, as controller and as processor, and shows missing mandatory details.
- Link: In every processing activity you pick the assets and systems from your inventory instead of typing them in.
- TOMs: For each of the 14 TOM areas under Art. 32 GDPR you see the linked controls and their status from your projects, for example ISO 27001 or NIS2.
Frequently asked questions
Does the GDPR require an asset register?
Not explicitly. Art. 30 GDPR requires the record, and Art. 32 GDPR appropriate measures for the processing systems and services. A register makes both verifiable, because you can show where a processing activity runs.
Do smaller companies need a record?
Art. 30(5) GDPR exempts companies with fewer than 250 employees, but only if the processing is not likely to result in a risk, is only occasional and does not include special categories of data. Payroll and customer management are not occasional, so in practice almost every company keeps a record.
Do risks have to be tied to assets?
The current ISO 27001 does not require it. Many companies still do it, because the owner and the protection requirements on the asset make the assessment easier.
How detailed does the register have to be?
Detailed enough that ownership and protection requirements are unambiguous. You can keep identical workstations as one group, while a server with personnel data has its own entry.
Do OT systems belong in the same register?
Yes, as far as they are in scope. Time recording terminals, cameras or access control systems on the shop floor often process personal data. The guide on the OT asset inventory shows how to collect OT assets without risk to the plant.
In a demo we use the demo company to show you how inventory and record work together.
Request a demo Try it for 14 days
Read more
- Guide "Building an OT asset inventory in six steps"
- Guide "Creating the ISO 27001 Statement of Applicability (SoA), with a template"
- Guide "ISO 27001 mandatory documents at a glance"
- Whitepaper on privacy operations
- Privacy operations: records, TOMs and data subject requests
- Asset management: inventory, zones and vendor advisories
- ISO 27001 in Complass
Not legal advice. This guide gives a general overview and does not replace an assessment of the individual case. The current wording of the GDPR and your licensed editions of the standards are authoritative. As of November 2026.