

Cyber Resilience Act checklist
CRA checklist for Annex I, Art. 13 and Art. 14
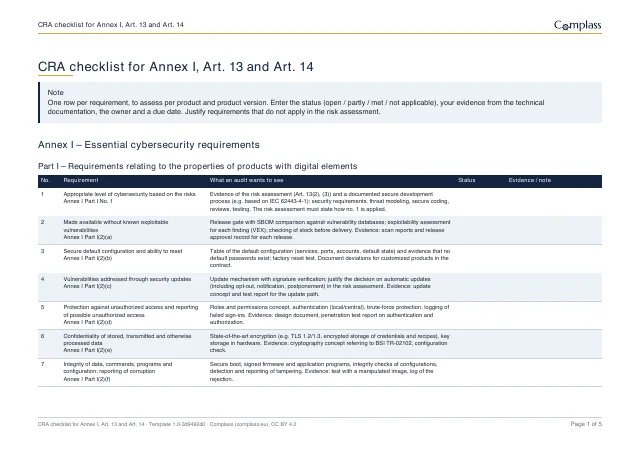
Annex I parts I and II plus the manufacturer and reporting duties of Art. 13 and 14, as a list to assess per product version.
What the file contains
32 requirements, one row each with area, reference and what an audit wants to see as evidence. You fill in the columns for status, evidence, owner and due date.
- Annex I – Essential cybersecurity requirements 22 rows
- Obligations of manufacturers and reporting obligations (Art. 13 and 14) 10 rows
Template version 1.0-3d9492d0 · content as of 12 November 2026 · Excel (XLSX) 105 KB · PDF 42 KB
This template is not legal advice. It does not replace checking which requirements apply to your company and does not guarantee any audit or certification result. License CC BY 4.0
How to use the file
Settle what applies
Assess per product and product version. Justify requirements that do not apply in the risk assessment.
Enter status and evidence
For each row a status (open, partly, met, not applicable) and where the evidence is.
Assign the gaps
Open rows get an owner and a due date. That turns the list into a plan.
The portal takes it from there
In Complass you assess the same requirements in the CE cyber file per product version, with SBOM, vulnerabilities and the reports under Art. 14.
- Guide Cyber Resilience Act for software makers: setting up SBOM, vulnerability handling and the 24-hour report
- Guide Does the CRA apply to me? Checking products with digital elements
- Guide CRA reporting duty for manufacturers: what Art. 14 requires and how to report
- Guide Technical documentation under the CRA: content and upkeep
- Guide CRA and IEC 62443: where they overlap and what is missing
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.