

This guide gives you a neutral criteria table, a weighted scoring example and a checklist. It also shows when a spreadsheet is still enough. The examples are invented.
What the law requires and what software contributes
The BSIG (German BSI Act) does not prescribe any software. It requires results you can prove:
- Measures: § 30(1) BSIG requires appropriate, proportionate and effective measures, and § 30(2) BSIG names ten areas they must cover at a minimum.
- Documentation: Under § 30(1) sentence 3 BSIG, compliance has to be documented.
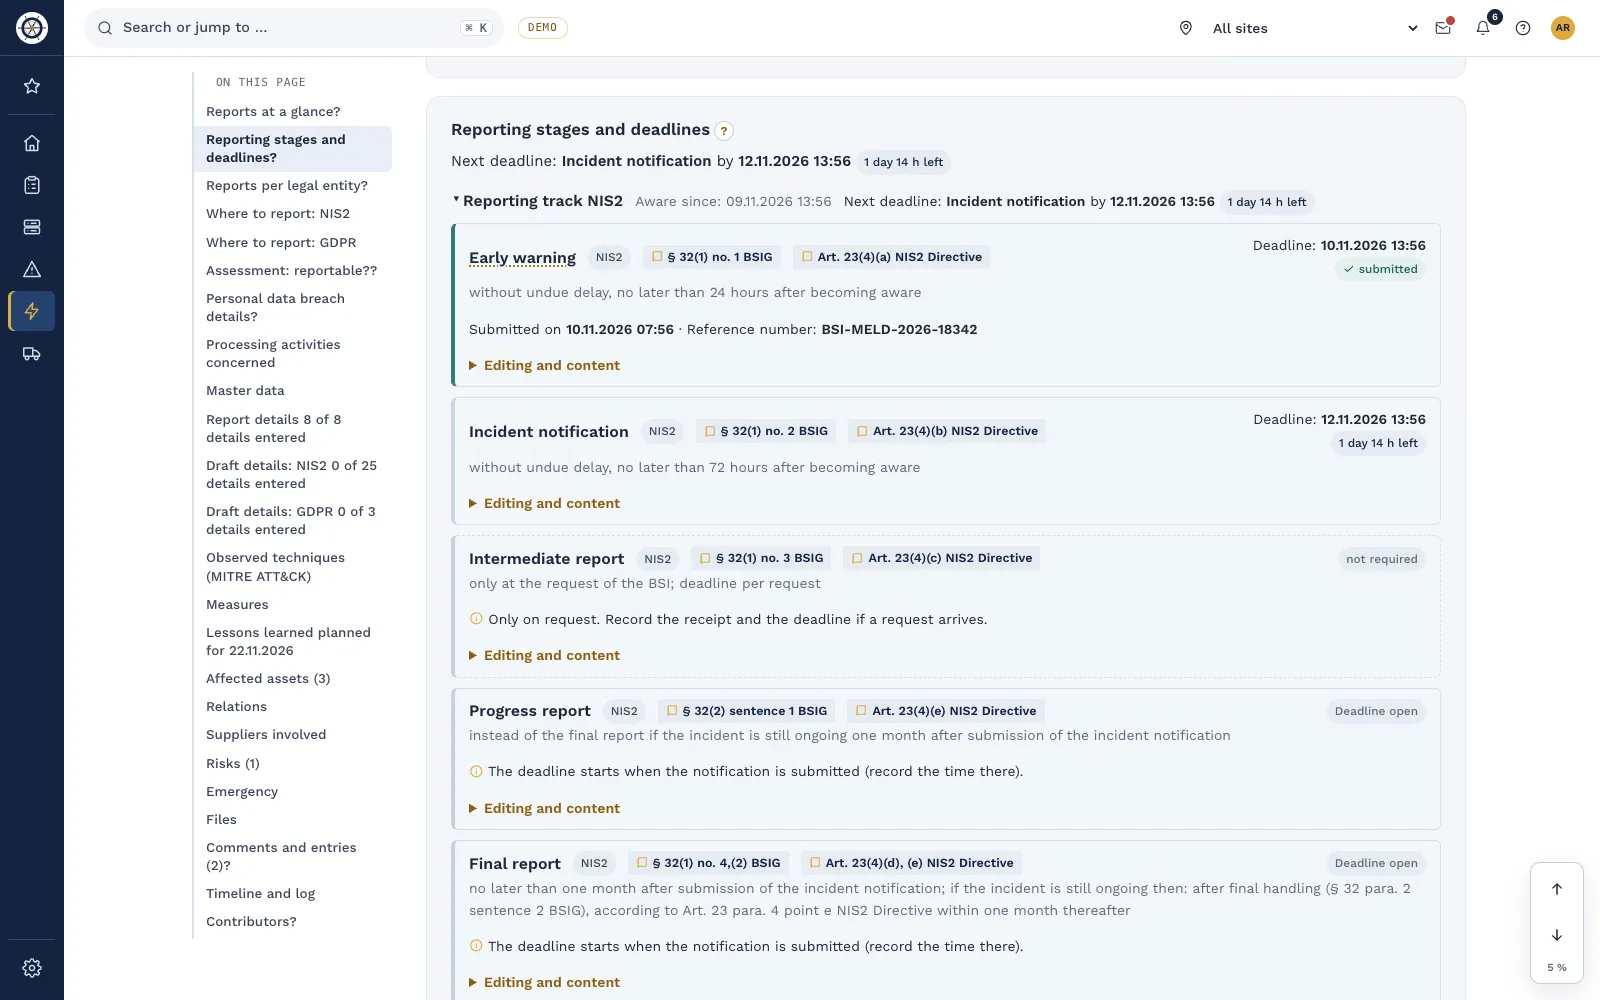
- Reporting: For significant incidents, § 32 BSIG requires an early warning within 24 hours, an incident notification within 72 hours and a final report one month after that at the latest.
- Management: § 38 BSIG obliges management to implement the measures, to oversee their implementation and to attend training regularly.
Software replaces none of these duties. It makes sure that status, ownership and evidence sit in one place and that you can show them at any time. That is the yardstick for every tool.
For certain types of digital entities, such as cloud providers and managed service providers, the requirements of the European Commission's Implementing Regulation (EU) 2024/2690 take precedence (§ 30(3) BSIG). ENISA has published technical implementation guidance on it, and the BSI explains the duties on its NIS-2 pages. If these requirements apply to you, check whether a tool maps them.
Choosing in six steps
- Bring the people together. The ISO, IT, OT or production, purchasing, data protection and one member of management. Each group names its three most important requirements.
- Set the knockout criteria. For example the hosting location, a processor agreement under Art. 28 GDPR or a complete export. A tool that fails here is out, however good it is otherwise.
- Weight the criteria. Spread 100 percent across the criteria in the table below. Whatever costs you the most time today gets the most weight.
- Test with your own cases. During the trial, run three real workflows: one measure with evidence, one supplier and one incident drill.
- Score separately. At least two people score independently. Discuss large differences together.
- Record the decision. Management decides and documents why. That is also evidence for § 38 BSIG.
The criteria at a glance
| Criterion | What you check | Question for the vendor |
|---|---|---|
| Measures under § 30 BSIG | All ten areas, per item applicability, status, evidence, owner and review cycle | How do you show me the status of a single measure with its evidence? |
| Evidence | Files with versions, second review, expiry date, links to other frameworks | Does one piece of evidence count for NIS2 and ISO/IEC 27001 at once, without a copy? |
| Reporting under § 32 BSIG | Decision "reportable or not" with reasons, deadlines from awareness, content per reporting stage | How does an incident run from suspicion to the final report? |
| Supply chain | Classification, questionnaire, supplier access, follow-up on gaps, review dates | Who maintains the supplier's answers, and what does their access cost? |
| Management under § 38 BSIG | Oversight, training records, confirmation by each member | How does management prove that it has overseen implementation? |
| Roles and permissions | Read and write per area, time-limited access, auditor access, MFA, single sign-on | Can an external auditor see only what they audit? |
| Hosting and data protection | Data center, processing agreement, subprocessors | Where are our data and the backups? |
| Export and switching | Reports as PDF and Excel, complete export in open formats | How do we get all our data if we switch? |
| Effort | Rollout, import of existing lists, ongoing upkeep, price over the term | How do we bring over our current spreadsheet? |
Keep in mind: the vendor of your NIS2 software is itself a service provider within the meaning of § 30(2) no. 4 BSIG. Assess it by the same standard as your other suppliers.
Example from mechanical engineering
The example is invented. A maker of packaging machines with 280 employees is classified as an important entity. Today the ISO keeps the measures in an Excel file, and supplier questionnaires go back and forth by email. The knockout criteria are a data center within the EU and a complete export. The team scores each criterion from 1 to 5 and compares two tools with today's spreadsheet.
| Criterion | Weight | Spreadsheet | Tool A | Tool B |
|---|---|---|---|---|
| Measures and evidence | 25% | 2 | 4 | 5 |
| Reporting process | 15% | 1 | 4 | 4 |
| Supply chain | 15% | 2 | 3 | 4 |
| Management | 10% | 1 | 3 | 3 |
| Roles and permissions | 10% | 1 | 4 | 3 |
| Hosting, data protection, export | 15% | 3 | 4 | 2 |
| Effort | 10% | 4 | 3 | 4 |
| Weighted total | 100% | 2.00 | 3.65 | 3.75 |
- Result: On points, tool B is slightly ahead. It is out all the same, because it offers no complete export.
- Lesson: Check knockout criteria before the points. Otherwise a tool wins that you could not use at all.
- Next: Management chooses tool A and records the reasons in the minutes.
When a spreadsheet is still enough
A well-kept spreadsheet is an honest start. It is enough as long as these points hold:
- One person maintains everything, and a deputy knows the file.
- You work with one framework and a small amount of evidence.
- You assess few suppliers and need no questionnaires for them.
- Management takes a verbal status report, and that is enough evidence for you.
The spreadsheet reaches its limits once several people work at the same time, evidence needs versions, questionnaires go back and forth by email or an incident triggers deadlines nobody may miss. Then you no longer look for the right row, but for the right file.
Checklist
- People from security, IT, OT, purchasing, data protection and management are named.
- Knockout criteria are set down in writing.
- The criteria are weighted and add up to 100 percent.
- All ten areas under § 30(2) BSIG can be mapped.
- An incident has been run as a drill during the trial.
- A real supplier has answered a questionnaire in the tool.
- Roles, auditor access and sign-in with MFA are checked.
- Hosting location, processing agreement and subprocessors are clear.
- A complete export has been tested.
- Management's decision is documented with its reasons.
How Complass meets these criteria
No more Excel file that only one person understands, and no more questionnaires in the inbox. Complass puts everything on one shared basis:
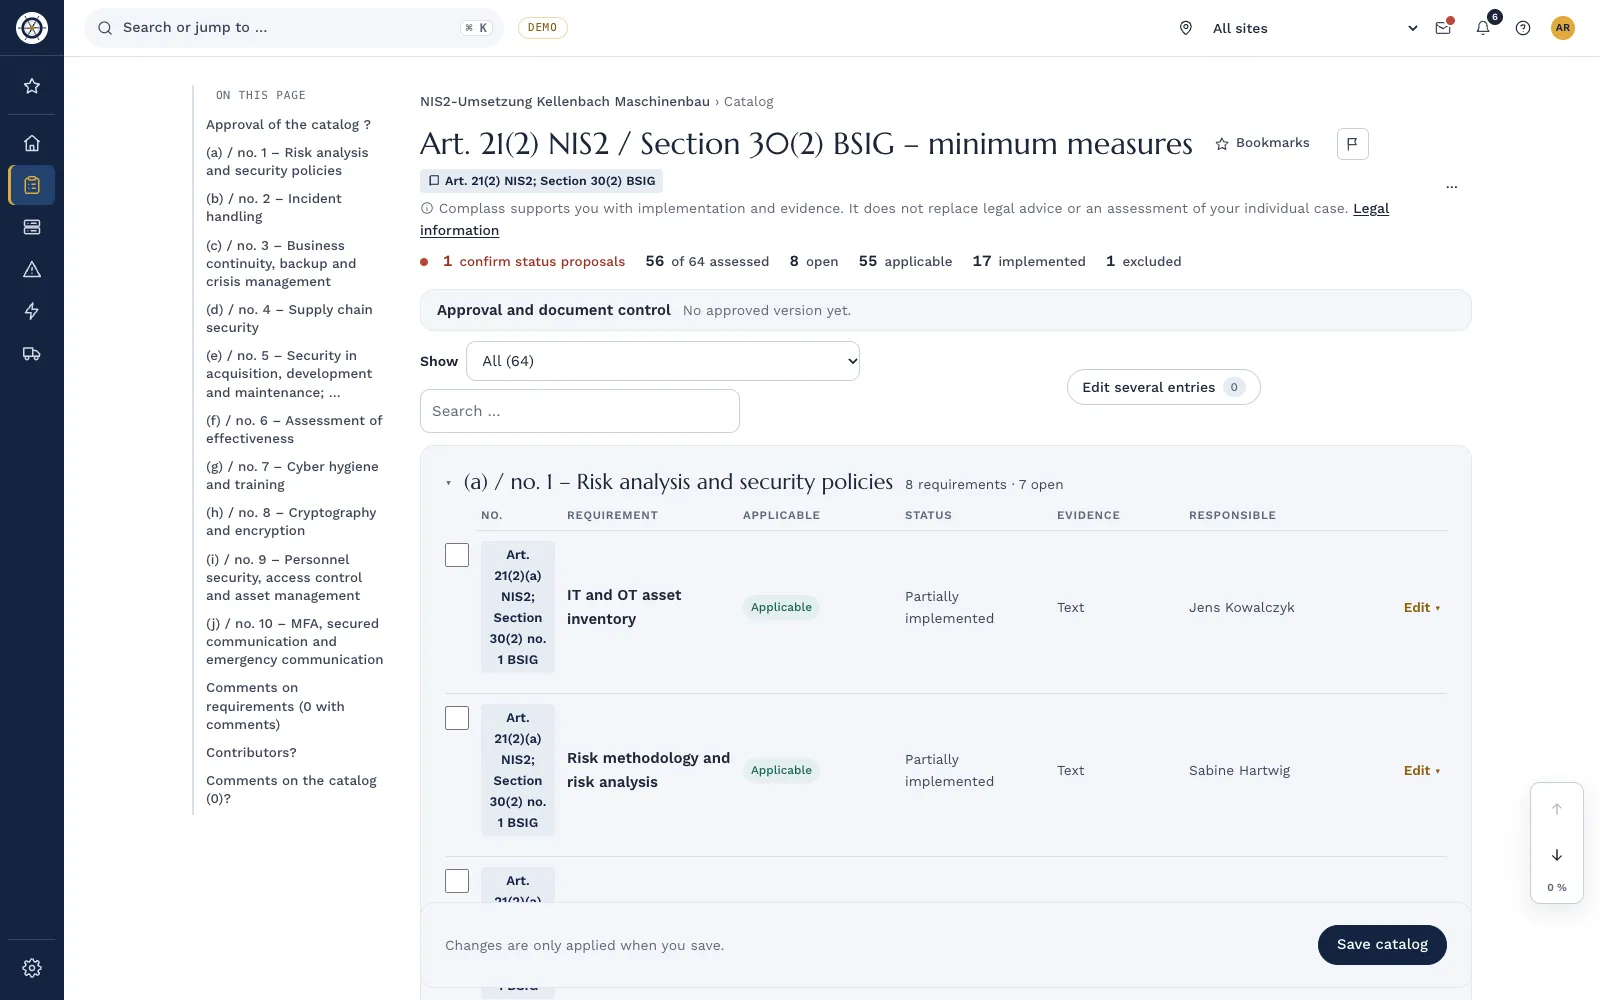
- Measures: The catalog for § 30 BSIG shows applicability, status, evidence and owner for each item. Link it with ISO/IEC 27001, and the evidence counts for both frameworks.
- Incidents: Guiding questions lead to a reasoned decision, and Complass calculates the deadlines under § 32 BSIG. You submit the report yourself in the authority's reporting portal.
- Suppliers: The supplier answers in their own free account and uploads evidence.
- Management: In the cockpit for § 38 BSIG, each member confirms oversight and training personally.
- Roles: Administrator, editor or read-only, plus permissions per area. You invite auditors for a limited time, with a log of every access. Sign-in with MFA, passkey or single sign-on.
- Hosting and export: Operated by Hetzner Online GmbH in data centers in Germany. When you switch to another provider, you get your data in open, machine-readable formats. The page "Switching provider and data export" describes what the full export contains.
- Getting started: You import your existing list of measures from Excel or CSV, with a preview before the import.
Frequently asked questions
Does the law prescribe specific software?
No. The BSIG requires measures, documentation, reports and oversight by management. You decide what you use to put that into practice.
Do we need separate NIS2 software if we already have an ISMS tool?
Not necessarily. Check whether your tool covers the areas under § 30 BSIG, the deadlines under § 32 BSIG and management's duties under § 38 BSIG. If something is missing, adding to it is often simpler than starting over.
How many tools should we compare?
Two or three on the shortlist are usually enough. Testing with your own workflows matters more than the number.
Does the software have to run in Germany?
The BSIG names no location. Check the hosting location as part of data protection and your own requirements. If they call for a specific location, make it a knockout criterion.
Who should make the final decision?
Management, based on the scoring. Under § 38 BSIG it is responsible for implementation and oversight.
In a demo we use the demo company to show you how measures, incidents, suppliers and the management cockpit work together. Or try it with your own cases.
Request a demo Try it for 14 days
Read more
- Guide "Implementing NIS2: a step-by-step guide"
- Guide "NIS2 without Excel: one portal instead of lists"
- Guide "NIS2 reporting duty in practice"
- Whitepaper NIS2
- NIS2 in Complass
- Compliance management
Not legal advice. This guide gives a general overview and does not replace an assessment of the individual case. The current wording of the BSIG is authoritative. As of November 2026.