

GRC platform or suite
Less rollout. More progress.
Large GRC suites can do a great deal and often need a rollout project of their own. Complass is a GRC platform with ready-made frameworks.
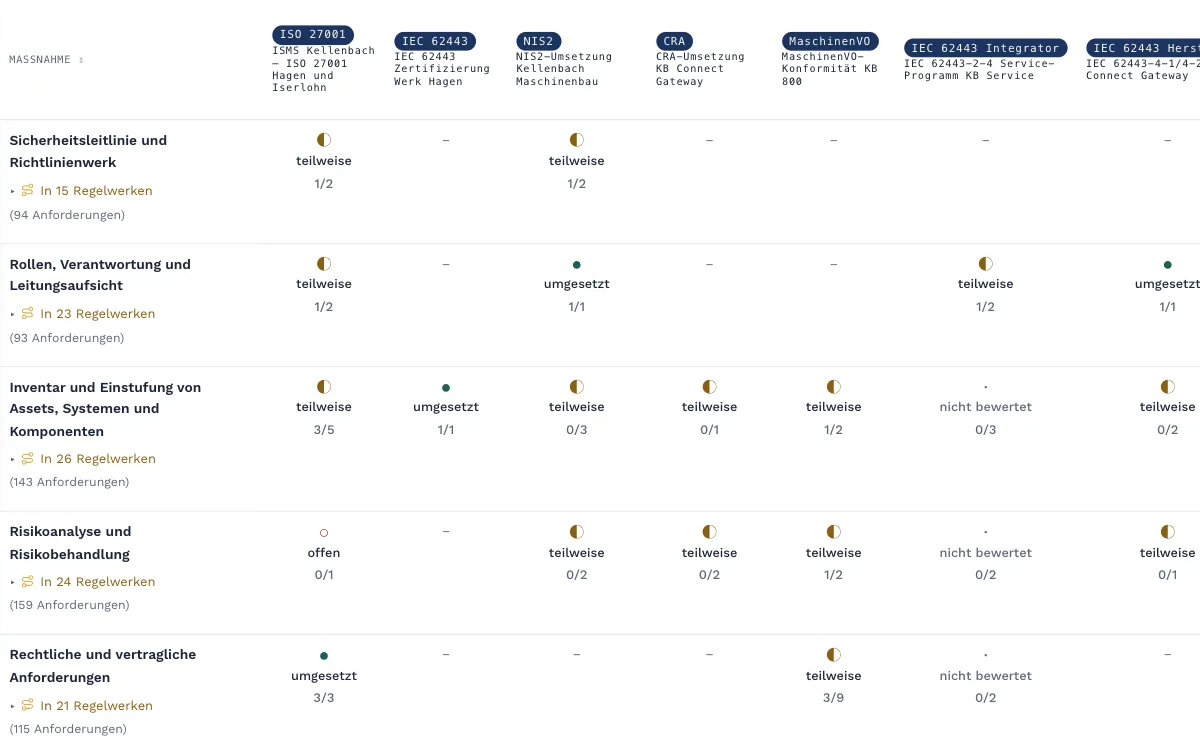
Two approaches compared
What differs day to day, point by point.
| Topic | Often with large GRC suites | With Complass |
|---|---|---|
| Getting started | A rollout project often sets up the data model, workflows and roles. | Frameworks are ready, with guidance texts and templates. You set up the trial yourself, with a sample project if you like. |
| Price | A quote often comes only after a sales call. | Packages and prices are published on the website. |
| Frameworks | Content often comes as an add-on or is entered during the project. | 26 frameworks can be booked. One measure counts for every framework that requires it. |
| Industry and products | OT and product security are often a matter of customization. | Zones and conduits per IEC 62443, the CE cyber file and CRA reporting are built in and bookable, no customization. |
| Day-to-day use | Many functions, often with training of their own. | Guided steps per framework. Platform trainings are included in every package. |
| Your data | Export often depends on the contract and the data model. | A complete export at any time in open formats, with a documented switching route. |
What GRC covers at Complass
Governance, risk and compliance in one data set. You maintain each piece of information once, and every measure counts for every framework that requires it.
Management and management review
Resolutions, oversight and training of management under Section 38 BSIG. The management review per clause 9.3 of the ISO standards with inputs, results as tasks and a personal confirmation by every participating member.
Risks with your method
A risk register with a matrix, qualitative, in euros or combined, with risk appetite and a treatment plan, linked to assets, vulnerabilities and incidents.
Internal audit for every framework
An audit program across the cycle, an audit plan and a checklist. Findings with root cause, corrective action and effectiveness check in one register.
Registers instead of spreadsheets
Interested parties, obligations, ISMS roles, findings, exceptions and certificates as registers, with owners and reminders of review dates.
Companies and sites
Companies with parent company and share, sites per company and permissions for a whole company. The group overview appears from two sites on.
Control tests every night
Every night Complass checks your data to see whether a measure is still backed by evidence, for example secure sign-in for all accounts or approved policies.
Which fits you?
A large suite fits better when …
- you want to run an internal control system for financial reporting or a group internal audit across all business processes in the same system.
- you want to design the data model and workflows largely yourself.
- a team of your own runs rollout and operation.
Complass fits better when …
- you want to steer and prove information security, NIS2, ISO 27001, the CRA, IEC 62443 or data protection as one program.
- management, departments and sites should work in the same system.
- your team implements itself and consulting comes in where it helps.
- you want to manage without an operations team of your own, because Complass runs the platform for you.
- you want to know the cost before anyone calls.
GRC stands for governance, risk and compliance. At Complass it covers information security, cybersecurity, product cybersecurity and data protection, not financial compliance.
Try Complass with your own data
Set up your trial yourself, with a sample project per framework if you like. If you would rather see Complass first, request a demo.