

Template based on ISO/IEC 27001
Information security policy
The top document of your ISMS, structured along clause 5.2 of the standard: fill-in guidance and a suggested wording for each section.
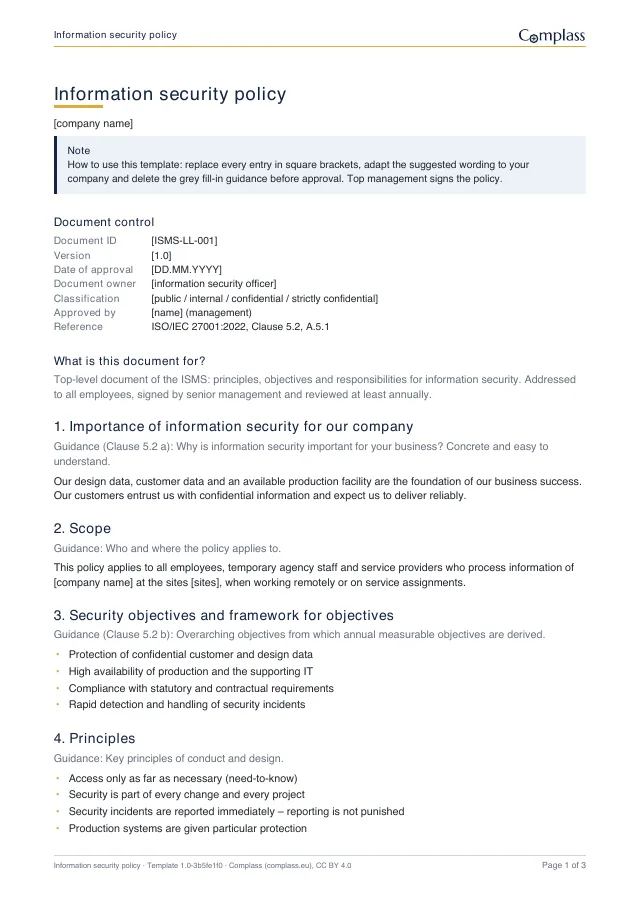
What the file contains
8 sections, each with fill-in guidance, the reference in the standard and a suggested wording you can keep or rewrite. Plus document control, a signature field and the change history.
- Importance of information security for our company Clause 5.2 a
- Scope
- Security objectives and framework for objectives Clause 5.2 b
- Principles
- Responsibilities Cl. 5.3
- Commitment to requirements and improvement Clause 5.2 c, d
- Handling of violations Clause 7.3, A.6.4
- Subordinate policies A.5.1
Template version 1.0-3b5fe1f0 · content as of 26 September 2026 · Word (DOCX) 6 KB · PDF 19 KB
This template exists in German and English; you get the English version.
This template is not legal advice. It does not replace checking which requirements apply to your company and does not guarantee any audit or certification result. License CC BY 4.0
How to use the file
Replace the brackets
Enter the company name, sites, roles and document control details.
Tailor the suggestions
The wording describes a company with production. Adapt the objectives and principles to your business and delete the grey guidance.
Sign and communicate
Top management approves the policy. Then all employees are told about it, and it is reviewed at least once a year.
The portal takes it from there
In Complass the policy is part of the ISO 27001 project: the same sections with fill-in help in the document, review and four-eyes approval, versions with checksum and acknowledgment by employees. The portal lists the subordinate policies itself.
- Przewodnik Information security in a small company: from spreadsheet to auditable evidence in 90 days
- Przewodnik ISO 27001 mandatory documents at a glance
- Przewodnik Creating the ISO 27001 Statement of Applicability (SoA), with a template
- Przewodnik ISO 27001 and NIS2: where they overlap
- Przewodnik Information security policy: outline and template
Przetestuj Complass na własnych danych
Mogą Państwo samodzielnie założyć konto testowe, na życzenie z przykładowym projektem dla każdej regulacji. Jeśli wolą Państwo najpierw zobaczyć Complass, proszę umówić demo.