


This guide shows which details matter, how to collect them without disturbing production and how the inventory stays current. The examples are invented.
Why the inventory is the foundation
- Risk assessment: IEC 62443-3-2 starts with the system under consideration. That assumes you know its parts.
- Zones and conduits: Every asset belongs to exactly one zone. Without a list there is no reliable zoning.
- Vendor advisories: An advisory on a firmware only helps if you know where that firmware runs.
- Incidents: People who can look things up in an emergency decide faster.
Frameworks ask for this overview as well. § 30(2) no. 9 BSIG (German BSI Act) names concepts for managing ICT systems, products and processes. ISO/IEC 27001 lists an inventory of information and other associated assets as control 5.9 in Annex A. IEC 62443-2-4 has an inventory register for service providers (SP.06.02), and IEC 62443-3-3 has a component inventory (SR 7.8).
Good guidance is free: "Foundations for OT Cybersecurity: Asset Inventory Guidance for Owners and Operators", published in August 2025 under the lead of the US agency CISA, with the German BSI as a co-author.
The six steps
- Set the scope. Decide on the site, plants and owners. Start with one important line instead of the whole factory.
- Gather what exists. Network diagrams, circuit diagrams, hardware configurations from the engineering tool, supplier documents and maintenance reports often supply most of it.
- Collect passively. A capture on a switch mirror port or OT monitoring shows devices and connections without loading the plant.
- Verify on site. Walk the plant, read type plates and record what does not show up on the network: service laptops, radio links, modems, unconnected devices.
- Classify. Assign type, criticality and zone to every asset and record dependencies.
- Settle the upkeep. Every change to the plant updates the inventory, including after an emergency repair.
Three ways of collecting compared
| Way | What you get | Limits | Risk to operations |
|---|---|---|---|
| Documents | Intended state, names, suppliers | Often out of date | None |
| Passive analysis | Devices, addresses, protocols and connections | Only sees what talks during the capture | Low, agree the setup with operations |
| Walkdown | Type plates, unconnected devices, remote access | Takes time | Low |
Take care with active scans: A network scan can disturb older controllers or fieldbus couplers. Use active methods only in agreement with operations, ideally in a shutdown window and with gentle settings.
Which details you need
Start small and complete. A short list that is right helps more than a long one with gaps. The fields follow our IEC 62443 module and the CISA guidance named above.
| Field | Example | What for |
|---|---|---|
| Name | PLC-FL1-01 | Clear identification |
| Type | Controller, HMI, switch, engineering station | Classification |
| Vendor and model | Sample vendor, model 3000 | Matching vendor advisories |
| Firmware or software | 2.3.0 | Matching vulnerabilities |
| Address and network | 10.20.1.15, VLAN 120 | Zones and connections |
| Location | Hall 3, line 1, cabinet 4 | Finding it in an emergency |
| Protocols | PROFINET, OPC UA | Planning conduits |
| Criticality | High | Setting priorities |
| Owner | Maintenance line 1 | Questions and upkeep |
Do not forget software: control system, databases, operating systems of operator stations and licenses all belong in it.
The inventory holds exactly the details a targeted attack needs. Classify it as confidential and settle who may see it.
Example from production
The example is invented. A beverage bottler starts with line 1. The diagrams show 38 devices. The capture shows 46. The walkdown finds a cellular modem from a machine supplier that nobody had on their list.
- Result: 47 assets, each with a zone and an owner.
- Visible at once: a remote access without approval and two operator stations without vendor support.
- Afterwards: The change request has a mandatory field "Inventory updated".
How the inventory stays current
- Part of the change process: No change counts as finished until the inventory is right.
- One responsible team: Usually control engineering or OT security, not "everyone".
- Regular comparison: Compare new captures with the inventory and clear up every unknown device.
- Confirmed state: Record when the inventory was last fully checked.
Checklist
- Scope and owners are set.
- Existing documents are evaluated.
- Passive collection is agreed with operations.
- Active scans are regulated or ruled out.
- The walkdown has recorded unconnected devices and remote access.
- Every asset has a type, zone, criticality and owner.
- Software and firmware versions are recorded.
- Changes reliably update the inventory.
- Access to the inventory is settled.
The inventory in Complass
A spreadsheet goes stale quietly, and nobody can see which row is still right. In Complass the inventory works for you:
- Import: You bring in Excel and CSV files, results from Zeek and Nmap and CSV exports from common OT monitoring tools.
- Captures: Your browser evaluates PCAP and PCAPNG files. The file does not leave your computer.
- No duplicates: All import paths match centrally. Unclear cases appear as "Possible duplicate: check".
- Discovered devices: New devices appear as candidates and never become assets automatically.
- Zones: You assign assets to zones under IEC 62443-3-2 and see them in the network map.
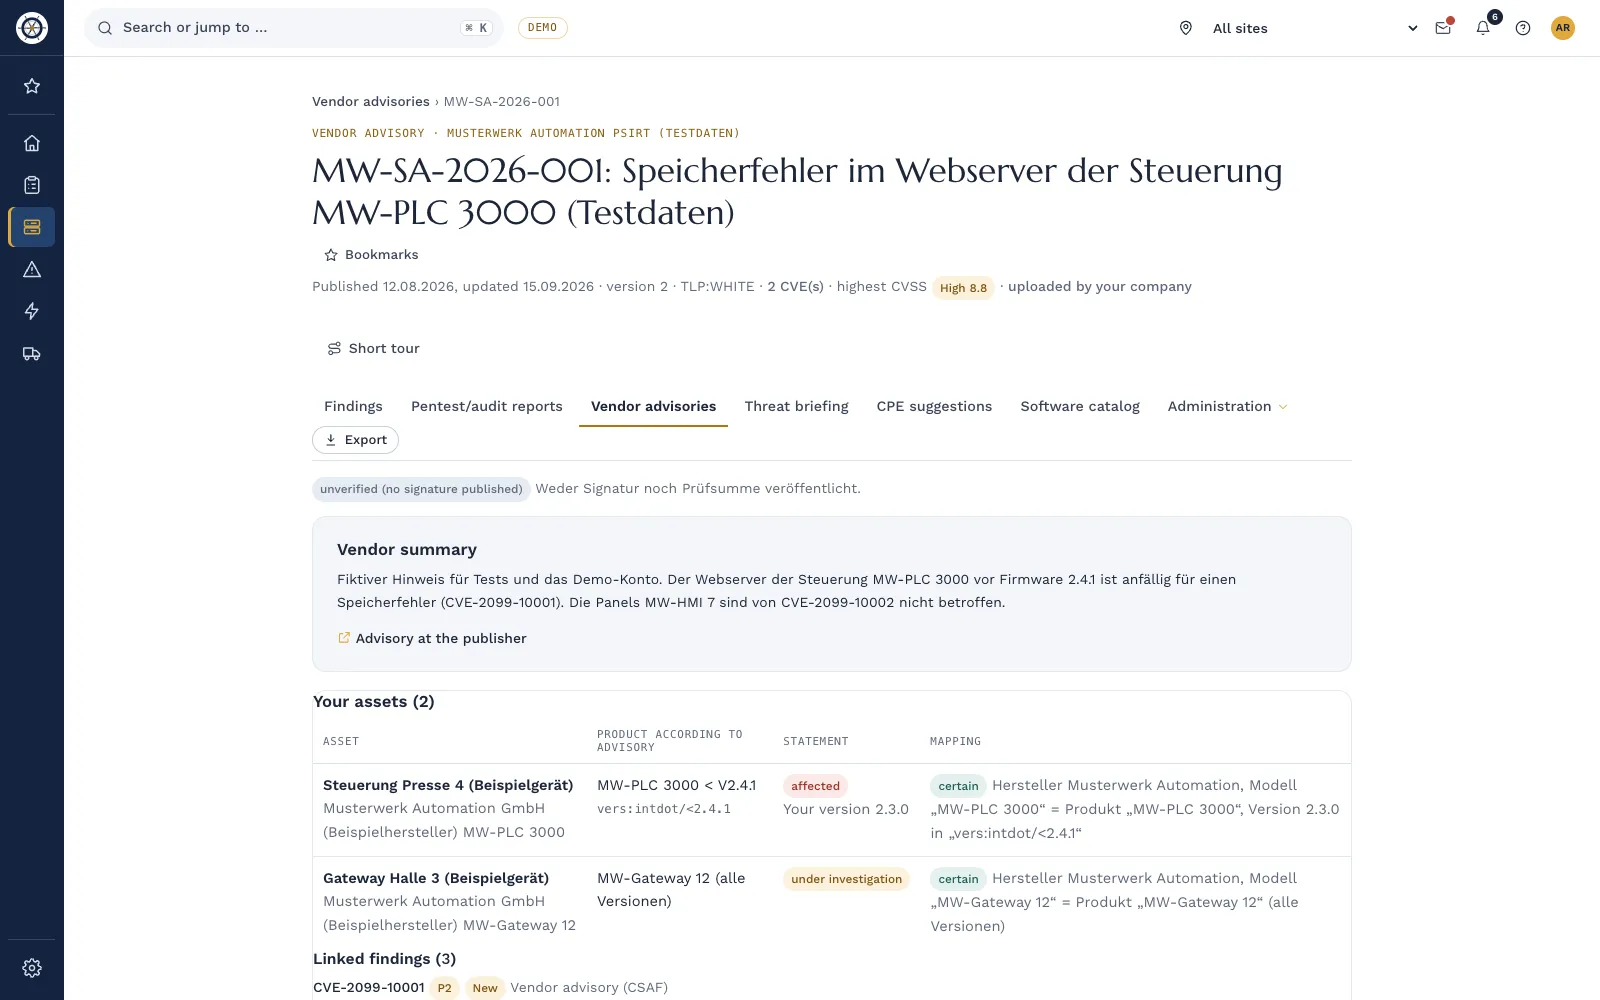
- Vendor advisories: Advisories in CSAF 2.0 are matched with the vendor, model and version of your assets.
Frequently asked questions
Can we start with Excel?
Yes, that is enough to begin with. It gets hard with upkeep, duplicates and matching vendor advisories. A well-kept spreadsheet can be imported later.
How complete does the inventory have to be?
None of the sources named here gives a percentage. What matters is that you set the scope and then cover it fully. Record gaps openly instead of hiding them.
May we scan in production?
Operations decides that together with you. Start passively. Use active queries only when agreed and, where possible, in a shutdown window.
Who should own the inventory?
Usually control engineering or OT security, because that is where the plant knowledge sits. IT helps with the network and tools.
Do supplier machines belong in it?
Yes, as far as they run in your plant. Also record who accesses them remotely.
In a demo we use the demo company to show you how a spreadsheet turns into an inventory with zones and vendor advisories.
Request a demo Try it for 14 days
Read more
- Guide "Zones and conduits in IEC 62443 explained"
- Guide "IEC 62443-3-2 risk assessment in seven steps"
- Whitepaper on assets, SBOM and vulnerabilities
- Asset management: inventory, zones and vendor advisories
- IEC 62443 in Complass
Not legal advice. This guide gives a general overview and does not replace an assessment of the individual case. The current wording of the BSIG and your licensed editions of the standards are authoritative. As of November 2026.