


This guide shows the stages, the criteria and a procedure that also holds at night and at weekends. The examples come from production and OT.
The stages at a glance
The reports go to the joint reporting desk of the BSI and the BBK, in practice through the BSI portal. The deadlines are upper limits: you report without undue delay.
| Stage | At the latest | Content | Reference |
|---|---|---|---|
| Early warning | 24 hours after becoming aware | Suspected unlawful or malicious acts, possible cross-border impact | § 32(1) sentence 1 no. 1 BSIG |
| Notification | 72 hours after becoming aware | Confirmation or update, first assessment with severity and impact, indicators of compromise where available | § 32(1) sentence 1 no. 2 BSIG |
| Interim report | At the request of the BSI | Relevant status updates | § 32(1) sentence 1 no. 3 BSIG |
| Final report | One month after submitting the notification | Detailed description, cause, remedial measures, cross-border impact where applicable | § 32(1) sentence 1 no. 4 BSIG |
| Progress report | Instead of the final report if the incident is still ongoing | Status at that time; the final report follows once handling is complete | § 32(2) BSIG |
In its instructions the BSI calls the second stage "Folgemeldung" (follow-up report). Operators of critical facilities also give details of the affected facility and the critical service (§ 32(3) BSIG).
An invented calculation: awareness on Monday at 2 pm means the early warning by Tuesday at 2 pm and the notification by Thursday at 2 pm. The one-month period starts only once the notification has been submitted.
When the deadline starts
The deadline runs from becoming aware of a significant incident. The BSI understands this as the moment an employee of the entity learns of it during working hours.
Decide internally how a report from the shift, maintenance or IT reaches the people who assess it. Record the time.
What counts as significant
A security incident impairs the availability, integrity or confidentiality of data or services (§ 2 no. 40 BSIG). Under § 2 no. 11 BSIG it is significant if one of these conditions applies:
- For your entity: It has caused or can cause severe operational disruption of the services or financial loss.
- For others: It has affected or can affect other natural or legal persons through considerable material or non-material damage.
Note the word "can": what matters is not only the damage that has occurred. § 2 no. 11 BSIG allows for a statutory ordinance with a more specific definition, so check whether one has been issued in the meantime.
Concrete criteria as orientation
For digital types of entity such as cloud and data centre providers, managed service providers or online marketplaces, Implementing Regulation (EU) 2024/2690 defines what is significant. For other sectors, according to the BSI, an incident counts as significant if at least one criterion from Art. 3(1) of this regulation is met:
- Financial loss: direct loss of more than EUR 500,000 or 5 per cent of annual turnover, whichever is lower.
- Trade secrets: exfiltration of trade secrets.
- Life and health: death or serious damage to a person's health.
- Unauthorised access: successful, suspectedly malicious access to network and information systems that can cause severe operational disruption.
In each case it is enough that the incident can cause this; unauthorised access must have happened and be capable of doing so. Point (f) of the article covers recurring incidents with the same cause (Art. 4), and point (g) refers to the criteria for the digital types of entity (Art. 5 to 14). The BSI also always assumes significance if critical services have failed or are impaired.
Examples from production
The examples are invented and show a first assessment, not a decision for your individual case.
| Event | Assessment | Why |
|---|---|---|
| Ransomware encrypts the MES, two lines stop | Probably significant | Severe operational disruption has occurred |
| Outside access to an engineering station through the remote maintenance access, machines keep running | Probably significant | Access has happened, is suspectedly malicious and can cause disruption |
| Design data leaves through a compromised account | Probably significant | Exfiltration of trade secrets |
| Phishing email is spotted, nobody enters data | Not significant | No impairment; at most a voluntary near miss in the portal |
| Line stops for a planned firmware update | Not a significant incident | Planned interruption, compare Art. 3(2) of the regulation |
The procedure in six steps
- Detect and record. Record when the entity became aware and what is known.
- Assess significance. The responsible person checks against your criteria and justifies the result, including "not reportable".
- Send the early warning. State what you know. According to the BSI, speed comes before completeness, and details can follow.
- Notify. Confirm or update the early warning and add the first assessment.
- Respond to questions. The BSI confirms receipt within 24 hours where possible and offers guidance on request (§ 36(1) BSIG).
- Close. Submit the final report or, while the incident continues, the progress report. Then review the incident internally.
What to settle in advance
- Assessment: Who decides on significance, and who deputises?
- Criteria: Translate the definition to your situation, such as outage time per line or access to controllers.
- Portal access: Who has their own certificate, and does access work without your own IT?
- Availability: The BSI recommends internal procedures that alert suitable people at night and at weekends as well.
- Service providers: They can be authorised to report, but responsibility stays with your entity.
- Exercise: Run through the procedure once, for example with an outage on a Friday evening.
Other reporting channels
One incident can trigger several duties. Align the content:
- Data protection: Art. 33 GDPR provides for notifying the supervisory authority within 72 hours in the case of personal data breaches.
- Products: Manufacturers of products with digital elements have their own reporting duties under Art. 14 CRA.
- Customers: The BSI can order you to inform the recipients of your services (§ 35(1) BSIG). Contracts can contain further duties.
- Other countries: The BSI is responsible for entities established in Germany (§ 59 BSIG). Check whether companies in other Member States have their own reporting duties there.
Checklist
- Own criteria for significant incidents defined.
- Assessing person and deputy named.
- Registration in the BSI portal completed, several people have access.
- Fallback route to the portal settled in case your own IT fails.
- Alerting outside business hours arranged.
- Report content prepared per stage.
- Coordination with data protection, sales and legal advisers agreed.
- Procedure practised once, improvements created as tasks.
Preparing reports in Complass
With a spreadsheet and email you track the assessment, deadlines and status of each stage yourself. In Complass everything sits on the incident:
- Assessment: Questions with their legal basis lead to a proposal per reporting channel. You record the decision and the reasoning yourself.
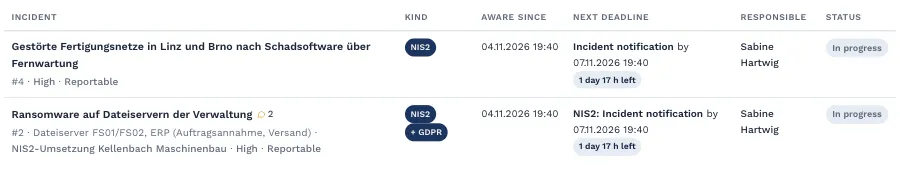
- Deadlines: The stages under § 32 BSIG appear with a calculated deadline, also in the calendar and in reminder emails.
- Report draft: Each stage shows a draft in the order of the BSI form, which you copy field by field.
- Several channels: You can add the GDPR channel to a NIS2 incident, for example, with its own stages and deadlines.
- Companies: If an incident affects sites of further companies, the reports appear per legal entity.
- Exercises: In a tabletop exercise you fill in the report draft with the watermark "EXERCISE – DO NOT SEND", without a real incident.
Frequently asked questions
Does Complass submit the report to the BSI?
No. Complass calculates deadlines, prepares content and documents. You submit the report in the BSI portal and enter the time and reference number in the incident.
Can we withdraw a report?
No. According to the BSI, a submitted report cannot be cancelled. You correct or add to it with a follow-up report.
We are not yet registered in the BSI portal. How do we report?
According to the BSI, entities in this case use the online form in the reporting and information portal (MIP). Operators of critical facilities and federal authorities use their existing reporting channels for the time being.
Do we have to report in German?
No. According to the BSI, reports may also be made in English. That helps international groups.
Who in our company may report?
The law does not prescribe a particular role. Anyone with access for your entity in the BSI portal can report. Even so, name fixed owners and deputies.
In a demo we use a sample incident to show you how assessment, deadlines and report draft come together in Complass.
Request a demo Try it for 14 days
Read more
- Guide "Implementing NIS2: the step-by-step guide"
- Guide "Registering with the BSI step by step"
- Whitepaper "When it has happened: reporting duties under NIS2, the CRA and the GDPR in one procedure"
- Incident management: recording incidents and checking the reporting duty
- NIS2 and the BSIG in Complass: applicability, duties and implementation
Not legal advice. This guide gives a general overview and does not replace an assessment of the individual case. The current wording of the BSIG and the requirements of the BSI are authoritative.