

Put compliance into practice,
even without experts in‑house.
One portal instead of spreadsheets. Assets, vulnerabilities and evidence arrive automatically from your systems, you decide.
Sound familiar?
A customer sends a security questionnaire.
Until now
The answers sit in three mailboxes, there are four versions of the list, and three colleagues are asked to check.
With Complass
- Import the questionnaire as Excel or CSV
- Take answers from your library
- Approve and export
Maintained once, used again and again.
Why Complass
Real relief in everyday work
Complass takes over collecting data and comparing lists. Your team looks after what is really open.
Automation
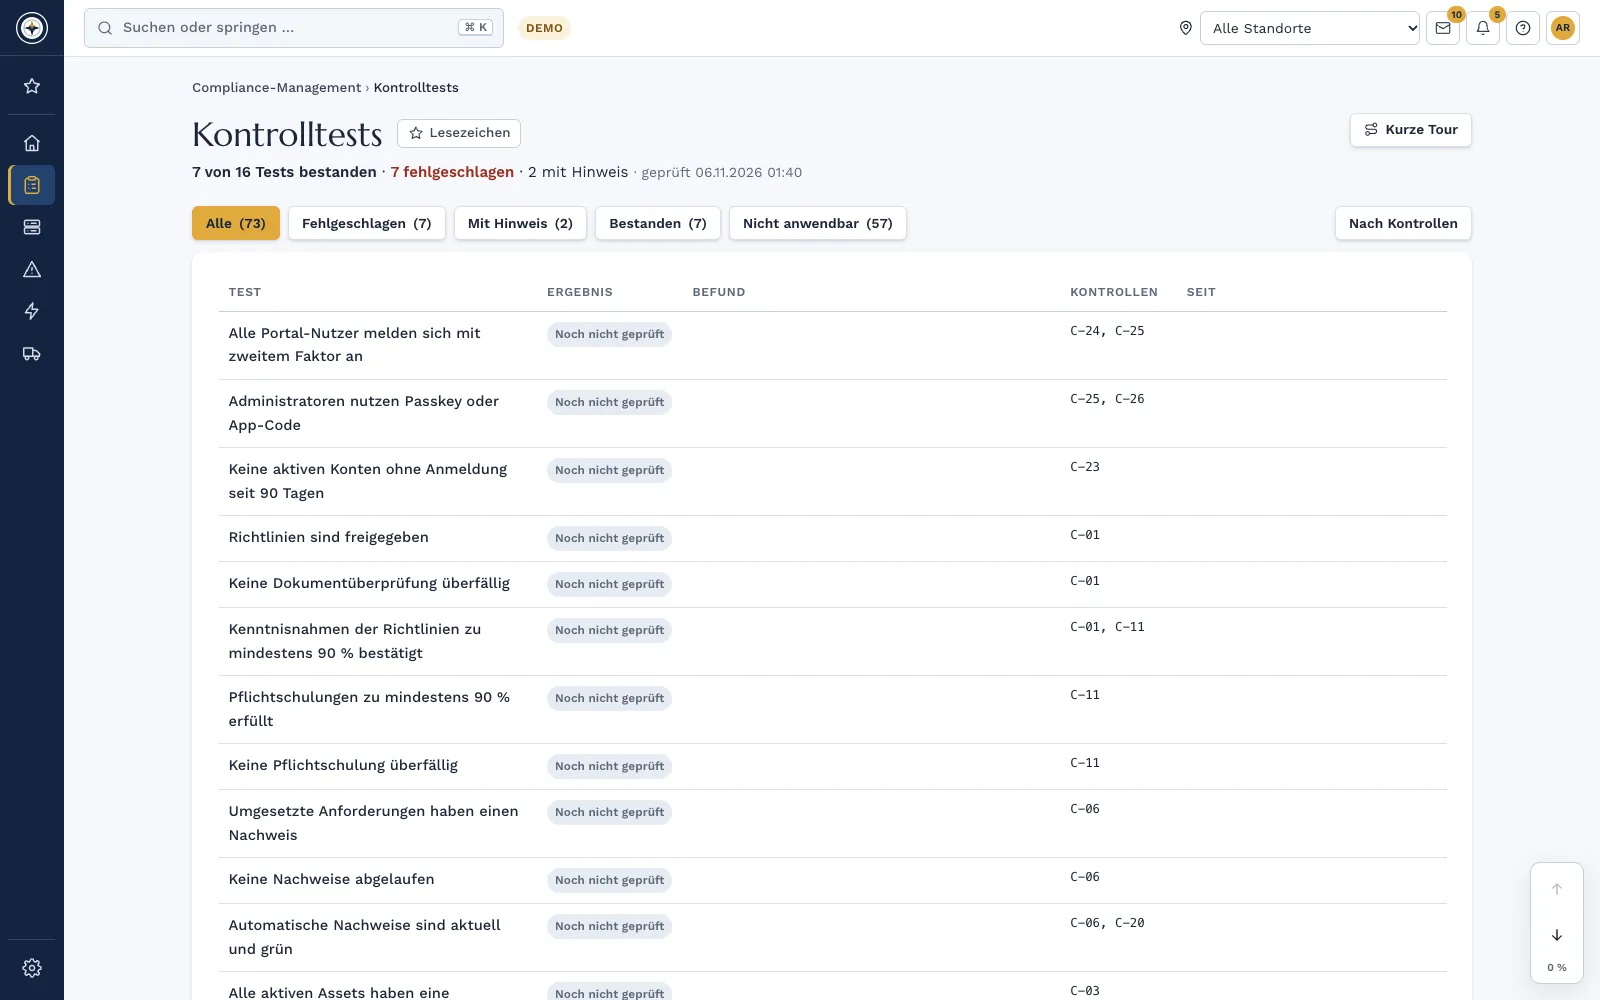
At night, Complass checks what is missing
Control tests and the rule check run over your state every night. In the morning you see what is open, without going through lists.
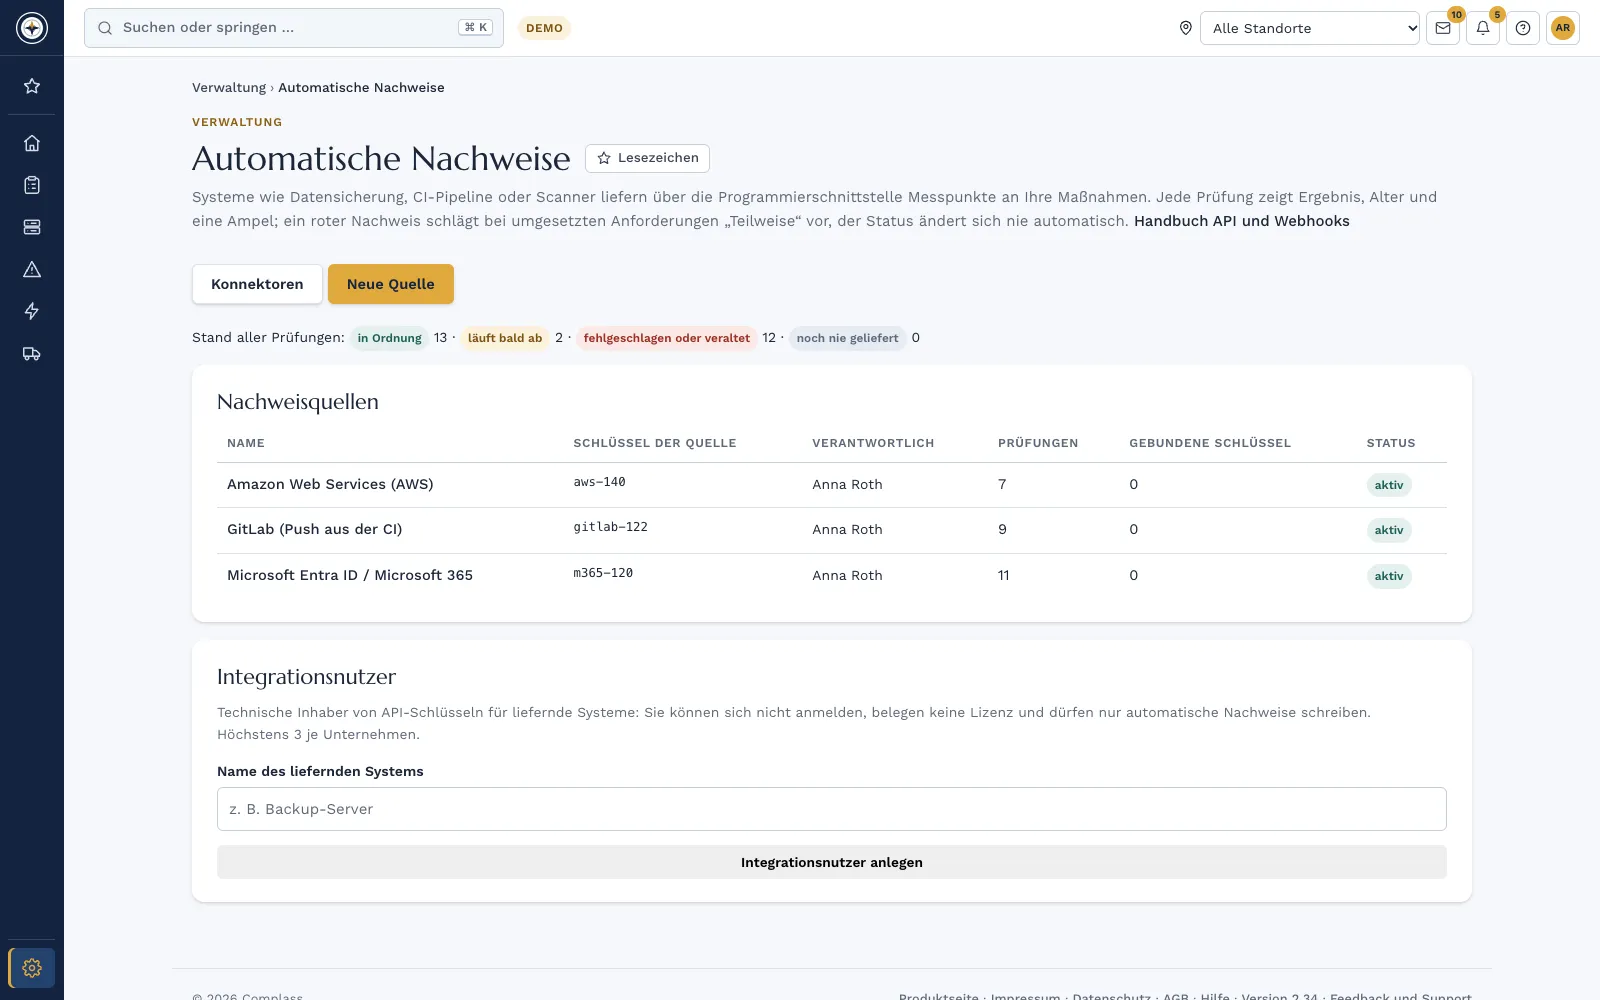
Connectors
Your tools deliver the data
Inventory, vulnerabilities and evidence come straight from your tools, without exports and follow-ups by email. For example from Microsoft 365, Jira, ServiceNow, Nozomi and NetBox.
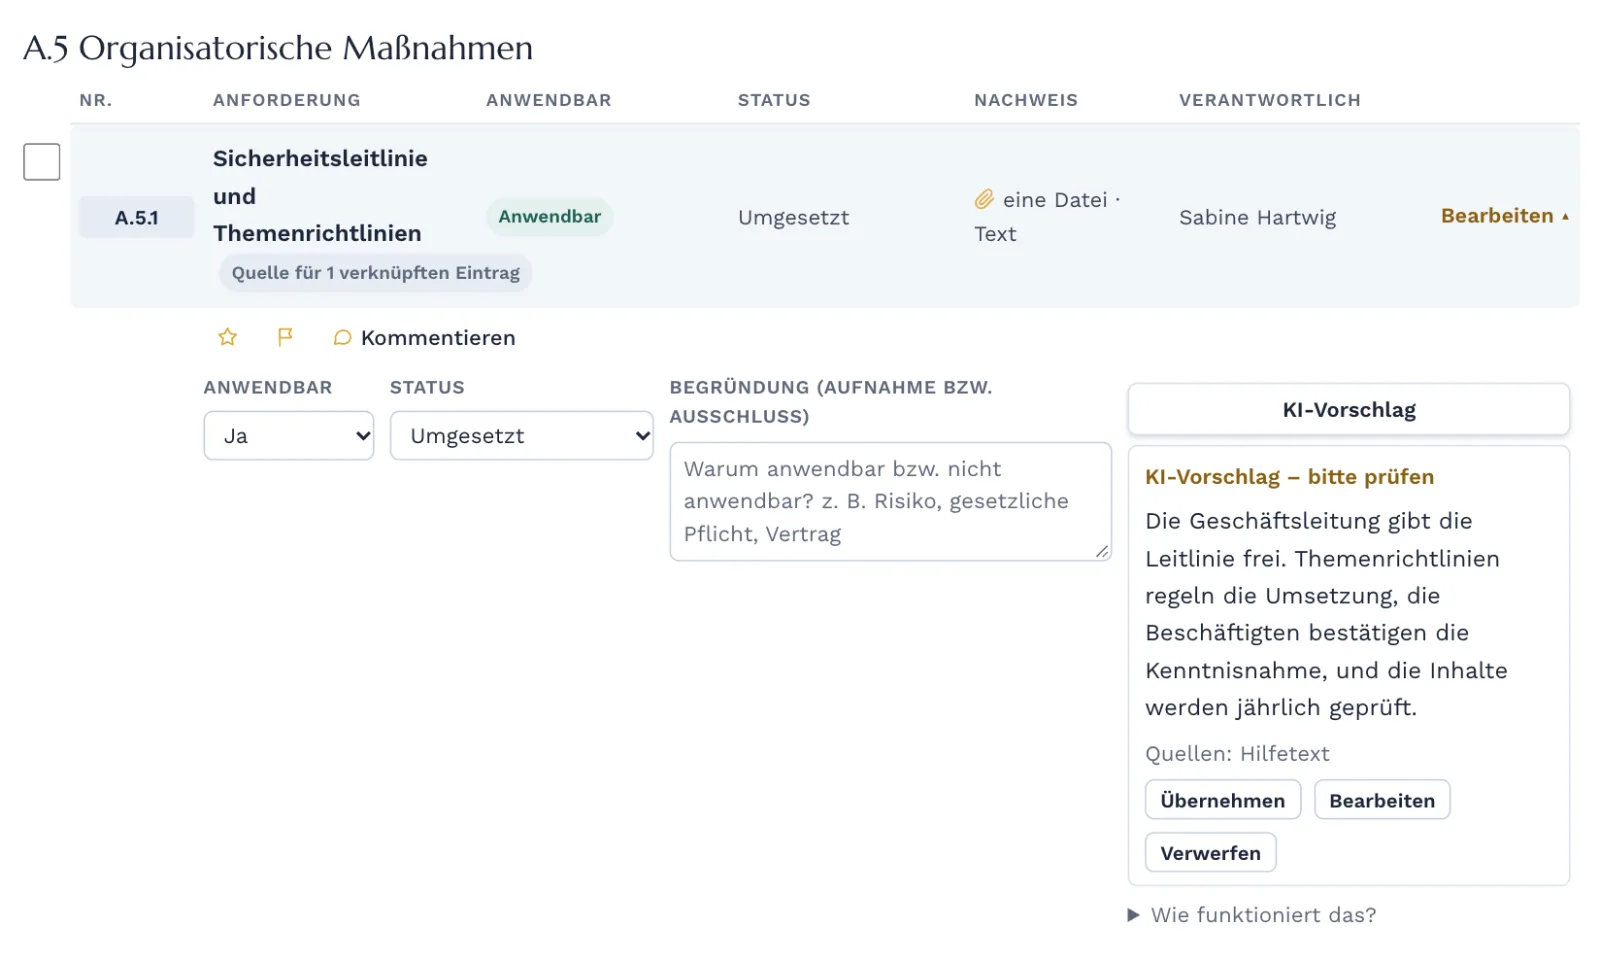
AI fill-in assistant Optional
Suggestions instead of empty fields
Suggested wording with sources from the legal text and the fill-in guidance. You decide; nothing is applied automatically.
This makes your everyday work even easier
- Works in your tools Deadlines, approvals and reporting duties appear in Teams or Slack.
- CE cyber file per product The CRA and the Machinery Regulation in one file per product and version: requirements, SBOM, vulnerabilities, support period.
- Supply chain at the push of a button Manufacturers release SBOM, VEX and security advisories once and share them with the customers they authorise.
- Alerting by SMS and voice For reportable incidents Complass reaches your incident team even at night and escalates to the deputy. Add-on.
- Customer questionnaires in minutes Import questionnaires as Excel or CSV, take answers from your library, approve and export.
- What has changed? The rule radar watches changes to your frameworks and shows what they mean for your programme.
Trademark notices
Product names and trademarks belong to their respective owners. There is no partnership, certification or endorsement by the owners. They only show which tools and formats Complass exchanges data with. Active Directory, Azure, Microsoft, Microsoft 365, Microsoft Defender, Microsoft Entra, Microsoft Intune, Microsoft Sentinel and Microsoft Teams are trademarks of the Microsoft group of companies. Jira is a trademark of Atlassian. Slack is a trademark of Slack Technologies, LLC. ServiceNow is a registered trademark of ServiceNow, Inc. GitHub is a trademark of GitHub, Inc. Elastic is a trademark of Elasticsearch B.V. Tenable Nessus is a registered trademark of Tenable, Inc. Nmap is a registered trademark of the Nmap Project. MITRE ATT&CK® is a registered trademark of The MITRE Corporation. CSAF is a standard of OASIS Open, the logo is from OASIS. XCCDF is a format of NIST SCAP; the NIST logo only names the format and does not mean a test, validation or endorsement by NIST. Grype logo by Anchore, CC BY 4.0.
One platform
One tool for all your compliance
One portal instead of many separate solutions: risks, measures, documents, assets, suppliers, incidents and training mesh together, and you maintain each piece of information only once.
- Platform and compliance
- Risk and operations
- Organisation and people
All modules
Platform and compliance
Risk and operations
Organisation and people
Everyone involved, in one portal: Your team, Supplier portal, Auditor portal, Partner portal. By your role under the law
Product
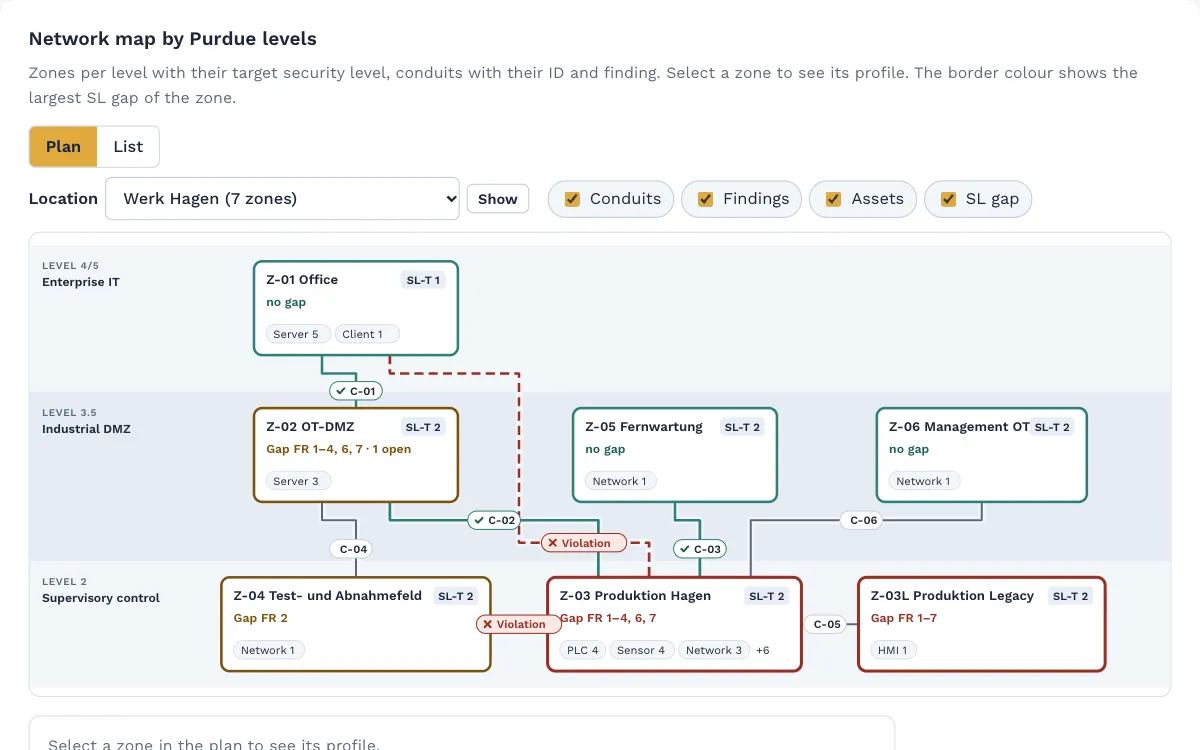
Complass in 90 seconds
Individual views to browse
The screenshots show the German interface.


Trust
Security you can verify
Your compliance documentation describes where your company is vulnerable. We protect it accordingly, and we describe exactly how.
OWASP ASVS 5.0
- Level 1
- 98 % Level 2
- 88 % Level 3
270 of 285 applicable requirements implemented
Each requirement assessed against the code and operations. We only call a level met once everything is implemented. Plus an automated penetration test. We are implementing Level 3 step by step where it adds protection for your data.
Self-assessment, as of 04.11.2026. We disclose three justified exceptions on levels 1 and 2 openly. Details · What this means for you
Get started
Start the way that suits you
Get started without training: an assistant sets up company, frameworks and team, then Complass guides you step by step to the evidence.
Transparent prices
The price is on the website
Packages, sizes and add-on modules are on the package page with their prices, without a sales call.
- Start
- €199
- Business
- €590
- Professional
- €890
Sample prices. Per month, size S, net, with annual payment
Try Complass with your own data
Implement it yourself
Complass explains every step in plain language, with templates and sample texts. Your consultant or auditor can work in the same portal when needed.
With support
Book workshops, setup and consulting directly from Complass or from one of our partners.
Factual and organisational support, no legal advice.